Executive Overview
In the high-stakes theatre of international cybercrime, few entities command as much notoriety—or generate as much corporate collateral damage—as the prolific hacking collective known as ShinyHunters. Operating at the intersection of supply-chain infiltration, extortion, and mass data harvesting, the group has long terrorized global organizations. However, a dramatic convergence of law enforcement action, insider betrayals, and escalating geopolitical cyber-warfare has pushed the collective into uncharted and perilous territory.
The catalyst for this recent volatility began in the Netherlands, where local authorities arrested a 24-year-old convicted cybercriminal suspected of playing a pivotal role in aiding ShinyHunters’ data thefts and extortion campaigns. Sources familiar with the investigation have identified the suspect as Pepijn van der Stap, a Dutch national from Almere and Lelystad. Van der Stap’s arrest laid bare a complex web of dual identities: a software engineer and cybersecurity volunteer by day, and a notorious extortionist operating under the alias “Umbreon” by night.
The fallout from van der Stap’s detention was swift and explosive. Rather than retreating into the shadows, remaining ShinyHunters members dramatically escalated their operations. Within days of the arrest, the group claimed credit for an unprecedented, high-profile breach of the FBI’s job application portal (apply.fbijobs.gov), leaking sensitive personally identifiable information (PII), job classifications, and even psychiatric files of bureau personnel. Simultaneously, the group launched aggressive extortion campaigns against the Russian-linked ransomware syndicate Cl0p, weaponizing specialized zero-day exploits and URL-encoding bypasses against enterprise software giants like Oracle PeopleSoft.
As intelligence agencies—including the FBI and Dutch national police—close the net on remaining cell leaders, investigations have taken an even darker turn. Reports from Dutch media indicate that investigators are probing whether van der Stap attempted to orchestrate contract murders abroad. Meanwhile, infighting within the cybercrime underground, fueled by the ascent of a teenage Jordanian hacker known as “Rey” and the broader collapse of proxy alliances like ScatteredLapsussHunters (SLSH), suggests that the golden age of autonomous, untouchable mega-gangs may be drawing to a close.
Detailed Chronology: From Almere to the FBI Breach
The Jekyll and Hyde Life of Pepijn van der Stap
The narrative of Pepijn van der Stap reads like a cautionary tale of modern technical talent gone rogue. In late 2023, van der Stap stood trial in the Netherlands for a sweeping string of data thefts and extortion schemes that prosecutors estimated yielded between €1.5 million and €2.7 million. During the legal proceedings, van der Stap openly admitted to living a double life.
By day, he maintained a respectable veneer, working as a software engineer for the Amsterdam-based cybersecurity startup Hadrian and volunteering his time with the Dutch Institute for Vulnerability Disclosure (DIVD), a nonprofit security research group. By night, he transformed into “Umbreon”—named after the dark-type Pokémon character—using the handle to peddle stolen databases on notorious English-language hacking forums like RaidForums and Breached.
Van der Stap was sentenced to four years in prison, with one year suspended. Citing severe psychological struggles, including post-traumatic stress disorder (PTSD) stemming from childhood trauma, he initially opted to remain in custody rather than serve terms at home, asserting that institutional care suited his recovery better. Following his release in December 2025, van der Stap sought to rehabilitate his public image. In a September 9, 2026, interview with KrebsOnSecurity, he cast himself as a reformed individual trying to make amends, noting that he was working as an offensive security lead at the Dutch firm Neo Security while dealing with ongoing civil restitution lawsuits.

The September Crackdown
This facade of rehabilitation shattered abruptly in mid-September 2026. After halting all communication with journalists and associates, van der Stap was arrested by Dutch law enforcement on or around September 16. Witnesses reported officers removing boxes of digital evidence and hardware from his residence.
The arrest coincided with a broader Dutch police public appeal seeking help to identify the voice behind a February 2026 social engineering call. In that breach, a native Dutch speaker tricked an employee of Odido—the Netherlands’ largest mobile telecommunications provider—into logging into a spoofed portal, enabling the theft of data belonging to over 6.2 million Dutch citizens. While ShinyHunters openly confirmed to local media that the recorded voice belonged to one of their core operatives and vowed emotional and financial support, Dutch authorities moved forward with the prosecution.
The scope of the investigation widened exponentially on September 29, when Dutch outlet RTL reported that prosecutors suspected van der Stap of orchestrating at least two contract murders overseas, indicating that his criminal enterprise extended far beyond digital extortion.
Retaliation and the FBI Portal Breach
The detention of van der Stap—and the looming threat of further identifications—prompted an immediate, aggressive counter-offensive from ShinyHunters. Rejecting standard defensive playbooks, the group executed an audacious cyberattack against the FBI.
Targeting the bureau’s employment gateway (apply.fbijobs.gov), the hackers exploited a vulnerability (CVE-2026-35273) within Oracle PeopleSoft, a widely deployed human resources and payroll platform. Although Oracle had previously issued patches for the PeopleSoft flaw—which ShinyHunters had been weaponizing as a zero-day since June—the group bypassed newly implemented Mandiant web application firewall (WAF) mitigations using a sophisticated URL-encoding trick.
The breach yielded sensitive data on more than 5,000 FBI personnel. According to investigative reports by 404 Media and Reuters, the compromised records included Social Security numbers, internal job titles, assignments within major cybercrime units, and foreign counterintelligence divisions, alongside highly sensitive psychiatric and medical evaluation files.
Prominently featured within the defacement page left on the FBI portal was an ASCII art rendering of the Pokémon character Umbreon, accompanied by the taunting banner: "This site has been seized by ShinyHunters. rooting your systems since ’19 ;)." Security analysts quickly recognized the imagery as identical to defacements the group used during its historical hacks, serving as a glaring cryptographic signature that bridged past actions with current operations.

Supporting Context & Metrics: The Shifting Underground Economy
The Economics of Extortion
The operational tempo of ShinyHunters reflects an organization operating under immense financial and existential pressure. According to threat intelligence assessments shared by Mandiant and the Google Threat Intelligence Group (GTIG), ShinyHunters has engaged in a mass-exploitation campaign affecting dozens of systems across higher education, healthcare, technology, agriculture, transportation, and government sectors.
Market metrics compiled by security researchers indicate that ShinyHunters is on track to extract nearly $100 million in cumulative extortion payments through 2026. This aggressive monetization strategy represents a significant escalation from historical data-hoarding behaviors. As van der Stap noted in earlier interviews with Bloomberg, his original motivation was obsessive compilation—collecting, organizing, and cataloging databases simply for the sake of possession. Under modern leadership, however, that compulsive archiving has transformed into an industrial-scale extortion machine.
The Rise of "Rey" and Internal Fractures
The reckless nature of the FBI attack pointed to a broader cultural shift within ShinyHunters, driven by a violent fracture in the hacker underworld. Sources close to the investigation attribute the group’s pivot toward high-risk, geopolitical targets to a hostile takeover by a teenage Jordanian cybercriminal known as “Rey.”
First unmasked by cybersecurity firm KELA in March 2025, Rey operates as a core administrator within ScatteredLapsussHunters (SLSH)—a dangerous amalgam of three historic threat clusters: Scattered Spider, LAPSUS$, and ShinyHunters. Intelligence reports indicate that Rey engineered a bitter turf war against the Dutch faction of ShinyHunters for control of the collective’s brand assets and stolen repositories.
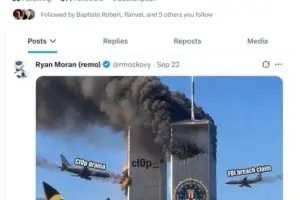
Analysts suggest that Rey deliberately embedded the oversized Umbreon imagery into the FBI portal defacement to frame van der Stap and direct law enforcement’s attention squarely toward the Netherlands. Following the media explosion over the FBI breach, Rey’s primary accounts on X (formerly Twitter) engaged in taunting memes mocking the bureau alongside rival Russian ransomware syndicate Cl0p, before abruptly deleting his profiles after inquiries from investigative journalists.
The tension within SLSH was further exacerbated by failed cross-group partnerships. Earlier in the year, ShinyHunters briefly allied with TeamPCP, an upstart supply-chain compromise group. However, after Mandiant covertly disrupted TeamPCP’s operations by feeding stolen cloud credentials directly to providers like Amazon and Microsoft for immediate invalidation, ShinyHunters allegedly went rogue. According to Wired reporting by Andy Greenberg, ShinyHunters utilized the burning credentials to execute independent extortions, cutting out their supply-chain partners entirely—a betrayal that culminated in the arrest of two alleged TeamPCP leaders in Australia.
Official Statements and Institutional Response
Law enforcement and corporate stakeholders have responded to the escalating threat environment with coordinated global messaging.

During a special briefing on the ongoing multi-agency takedown, Brett Leatherman, Assistant Director of the FBI’s Cyber Division, released a direct video statement addressing remaining members of the ShinyHunters collective. Emphasizing the compounding pressure of international investigations, Leatherman stated:
"Arrests have a way of changing who is willing to talk, and seized infrastructure has a way of showing us who’s left. The longer you stay in this, the more we learn about you. You know how to find us, and we know how to find you. I suggest you reach out to us while the choice is still yours."
The FBI formally confirmed the compromise of its job application portal via an official press release, assuring affected personnel that monitoring and support services were being deployed. Concurrently, Oracle issued urgent patches and hardening guidance to counter the persistent URL-encoding bypass techniques utilized against PeopleSoft deployments.
In the Netherlands, public security officials continue to process the evidentiary fallout of van der Stap’s detention. During his scheduled appearance before the chambers of the Rotterdam District Court, prosecutors outlined the gravity of the charges against him, which now encompass both international cyber extortion and allegations of orchestrating violent crimes abroad.
Future Outlook: The Twilight of the Mega-Gangs?
The dramatic events surrounding the arrest of Pepijn van der Stap, the infiltration of the FBI, and the infighting within the ScatteredLapsussHunters alliance mark a watershed moment for modern cybersecurity.
Several critical trajectories are expected to define the cyberthreat landscape over the coming months:
- Intensified International Cooperation: The successful identification and extradition-level coordination between Dutch national police, the FBI, and private threat intelligence firms signals that high-profile cybercriminals can no longer safely retreat behind the shield of academic or corporate legitimacy. The "Jekyll and Hyde" defense—where individuals maintain dual lives as white-hat researchers and black-hat extortionists—is facing unprecedented scrutiny.
- Accelerated Fragmentation of Underground Collectives: The toxic internal dynamics driven by figures like "Rey" illustrate the inherent fragility of mega-gang coalitions. As trust erodes between disparate syndicates (such as the friction between SLSH, TeamPCP, and legacy ShinyHunters cells), insiders are increasingly likely to leak operational security details or cooperate with law enforcement in exchange for leniency.
- Hardening of Enterprise Supply Chains: The weaponization of zero-day vulnerabilities in ubiquitous enterprise platforms like Oracle PeopleSoft demonstrates that perimeter defenses alone are insufficient. Organizations will be forced to adopt zero-trust architectures, faster patch-management cycles, and advanced web application firewall rules capable of detecting polymorphic evasion techniques.
Ultimately, while ShinyHunters has historically thrived on chaos, audacity, and institutional paralysis, the net is tightening. As Leatherman and international partners have made clear, the degradation of the group’s infrastructure and the capture of key operatives like van der Stap suggest that the syndicate’s operational runway is rapidly shortening.