Executive Overview
In a decisive move to dismantle the financial infrastructure facilitating Russia’s wartime economy and international cybercrime, the United Kingdom has levied sweeping economic sanctions against Cryptomus. Known as a "chameleonic" cryptocurrency payment platform, Cryptomus has long served as a digital tollbooth for ransomware syndicates, darknet narcotics markets, online fraud operations, and illicit services designed to help the Russian state evade international financial restrictions.
Announced on October 8, the U.K. Treasury’s sanctions freeze any assets held by Cryptomus within British financial institutions and bar UK-based companies, individuals, and virtual entities from conducting any business with the platform. Alongside Cryptomus, the U.K. government targeted several associated digital asset payment processors, including VexPay, TokenSpot, and the Tsunami Payments service.
While Canada previously attempted to penalize the platform with a record-breaking CAD $176 million fine in late 2025 for severe anti-money laundering (AML) violations, security experts and blockchain investigators note that financial penalties alone are often toothless against brazen, cross-border digital crime syndicates. By upgrading penalties to full economic sanctions, London has executed a far more lethal blow: unlike monetary fines, targeted sanctions legally prohibit engagement, cutting off vital access to Western financial liquidity and systematically dismantling the operational mechanics of evasion networks.
The crackdown also marks a historic milestone in international regulatory enforcement. According to blockchain forensics experts, this represents the first documented instance of a "Five Eyes" intelligence-sharing nation (comprising Australia, Canada, New Zealand, the United Kingdom, and the United States) officially sanctioning a cryptocurrency entity incorporated within another Five Eyes jurisdiction—underscoring the borderless threat posed by shell-company regulatory arbitrage.
Detailed Chronology: Evolution of a Cybercrime Conduit
To fully understand the scale of the operation brought down by British authorities, one must trace the timeline of Cryptomus and its corporate iterations, which reads like a masterclass in corporate evasion and regulatory shell games.
Emergence and Early Growth (2022–2023)
Cryptomus officially burst onto the digital finance scene in 2022. Operating quietly as a merchant-facing crypto-payment gateway, the platform quickly gained traction among Russian cryptocurrency exchanges and online storefronts peddling illicit services, hacking tools, and stolen data. Behind the scenes, the company was tied to corporate entities such as Certa Payments and Xeltox Enterprises, utilizing heavily obfuscated ownership structures and virtual office addresses.
Notably, investigations revealed that Cryptomus shared a physical corporate registration address in Vancouver, Canada, with dozens of other foreign currency dealers and money transfer businesses—none of which maintained an actual physical presence at the location. Despite its paper-thin veneer of legitimacy, the platform processed billions of dollars in untracked cryptocurrency, quietly positioning itself as a premier laundering conduit for Russian financial institutions seeking to bypass Western sanctions following the invasion of Ukraine.
The Canadian Crackdown and the Birth of "Heleket" (2024–2025)
As investigative reports by cybersecurity journalist Brian Krebs and blockchain analytics firms began mapping out Cryptomus’s infrastructure, regulatory bodies closed in. In December 2024, deep-dive investigations highlighted how Cryptomus functioned as the primary bridge converting illicit crypto into cash inside Russian banks.
Faced with mounting scrutiny, Cryptomus briefly instituted superficial "Know Your Customer" (KYC) rules, causing a temporary dip in transaction volume. However, the platform quickly pivoted back to its core illicit user base.
In October 2025, the Financial Transactions and Reports Analysis Centre of Canada (FINTRAC) dropped a historic hammer, issuing a record CAD $176 million fine against Cryptomus for sweeping AML violations. Rather than paying the penalty or reforming its practices, Cryptomus launched a blatant evasion strategy: it appealed the fine, quietly abandoned its primary storefront, and spun up a parallel, no-KYC operational twin named Heleket. Telegram support channels and technical artifacts confirmed that Heleket operated as a direct continuation of Cryptomus, serving the exact same clientele while ignoring international subpoenas and regulatory edicts.
The British Hammer Falls (October 2026)
By late 2026, the cumulative toll of unregulated, high-volume criminal transactions processed by the platform forced Western allies to rethink their enforcement strategies. On October 8, 2026, the U.K. government officially designated Cryptomus, TokenSpot, VexPay, and Tsunami Payments under its Russia sanctions regime.
The immediate impact was visceral. Within hours of the announcement, users attempting to access payment processing infrastructure were met with automated error messages. Telegram support bots for both Cryptomus and its spin-off Heleket abruptly went offline or began posting frantic denials of affiliation, claiming the platforms were suddenly unable to process transactions as blockchain intelligence firms rushed to blacklist newly identified wallet clusters.

Supporting Context & Metrics: The Scale of Illicit Volume
The narrative that Cryptomus was a minor player or a misunderstood startup is thoroughly dismantled by hard on-chain data compiled by leading blockchain intelligence institutions. The sheer volume of illicit capital channeled through its network places it in the upper echelon of cybercrime financial infrastructure.
Multi-Billion Dollar Flow
In an April 2026 intelligence report, blockchain analytics firm TRM Labs revealed that Cryptomus had processed an astonishing $7 billion in cumulative transactions since its inception in 2022. This staggering volume was not confined to routine commercial e-commerce; TRM Labs explicitly tied a significant portion of these transactions to abhorrent criminal ecosystems, including:
- Vendors distributing Child Sexual Abuse Material (CSAM).
- International terrorist financing networks.
- Cross-border human trafficking rings.
- Advanced ransomware syndicates targeting Western critical infrastructure.
Surpassing Traditional Mixers
Furthermore, blockchain data crunching firm Chainalysis highlighted the structural shift represented by platforms like Cryptomus in their October 8, 2026 analytical brief. Chainalysis noted that Cryptomus and its sibling network Heleket evolved into primary liquidity hubs for illicit activity on a scale that dwarfed traditional crypto-mixing services.
According to Chainalysis telemetry, the aggregate volume of illicit funds received by Cryptomus/Heleket across tracked categories surpassed all traditional cryptocurrency mixers combined within the dataset. At its peak in late 2025, the number of distinct illicit counterparties interacting with the platform surged to more than 900 entities in a single month, illustrating an industrial-scale laundering operation integrated directly into the digital underground.
Official Statements and Expert Perspectives
The enforcement action has elicited strong reactions from the cybersecurity community, highlighting the fundamental difference between regulatory fines and targeted asset freezes.
Richard Sanders, a veteran blockchain investigator and analyst who spent months mapping out the inner workings of Cryptomus’s payment rails and interacting directly with its merchant ecosystem, emphasized why the British intervention is a game-changer.
Writing on professional networks following the announcement, Sanders pointed out the fatal flaw in Canada’s earlier regulatory enforcement:
"A fine doesn’t stop a cryptocurrency payment processor from processing payments. Sanctions kill the operation. The distinction matters."
Sanders noted that because Canada’s CAD $176 million fine was ultimately uncollectible from an entity operating fluidly across shadowy digital jurisdictions, Cryptomus simply laughed off the penalty, appealed indefinitely, and launched Heleket as an operational carbon copy. By contrast, a sovereign economic sanction criminalizes interactions with the network, compelling global financial institutions, liquidity providers, and web hosting services to instantly sever ties or face catastrophic regulatory liability.
Chainalysis echoed this sentiment in their official advisory, characterizing the sanctions as a vital surgical strike against the structural foundations sustaining the Kremlin’s war machine:
"Cryptomus and Heleket have emerged as major payment hubs for illicit activity. The U.K.’s actions target the broader, highly resilient infrastructure supporting Russia’s wartime economy, cutting off essential pipelines that allow illicit funds to convert seamlessly into fiat currency."
The Phantom Regulator: Tracing the Roots to Western Sahara
Perhaps the most bizarre and illuminating aspect of the Cryptomus enterprise lies in how it legitimized itself on paper. Where do unregulated, fly-by-night payment platforms operating out of Western jurisdictions derive their purported legal authority to handle billions of dollars in international funds?

The answer exposes a glaring loophole in global corporate registration: a web of fake financial institutions overseen by a phony regulatory body positioned within a disputed territory that lacks general international recognition as a sovereign state.
The Western Sahara Shell Game
Detailed forensic investigations into Cryptomus’s corporate parent, Certa Payments, revealed that its sole shareholder was a 25-year-old Ukrainian woman. Beyond managing Certa Payments, this individual served as the head of several interconnected shell corporations, including the WS Management and Advisory Corporation.
WS Management and Advisory Corporation billed itself as an official, exclusive regulatory body responsible for issuing licenses to cryptocurrency exchanges, foreign exchange (Forex) brokers, and online gaming operations. However, there was a glaring catch: its jurisdiction was claimed to be the Western Sahara—a disputed and largely unrecognized territory in northwest Africa.
Exposing Crasadr.com
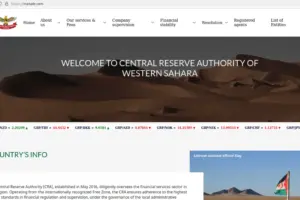
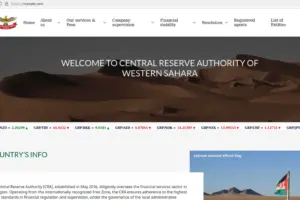
Investigators uncovered that the regulatory body operated out of a website domain named crasadr.com, purporting to represent the Central Reserve Authority of the Western Sahara (CRASADR). The portal listed various fraudulent entities that had allegedly been granted regulatory approval to conduct global financial transactions.
Digital infrastructure analysis further solidified the deception. One of Certa Payments’ former legacy web domains (certa.website) was found sharing a physical server cluster with 12 other domains. Among them was rasd-state.ws, explicitly utilized as a portal for the nonexistent Central Reserve Authority.
By weaponizing obscure geographic disputes and setting up paper regulatory bodies in unrecognized territories, operators behind Cryptomus successfully gamed standard international corporate registries. They secured nominal corporate standing in Western nations while answering to a phantom regulator impervious to international legal subpeonas.
Future Outlook: The End of the Line for Chameleonic Gateways?
The U.K. Treasury’s sanctions against Cryptomus, Heleket, TokenSpot, and VexPay signal a definitive shift in how Western governments intend to combat crypto-enabled sanctions evasion and cybercrime.
For years, bad actors relied on a playbook of corporate metamorphosis: when one shell company or exchange was exposed, fined, or pressured, they would simply rebrand, spin up a new domain, launch a parallel platform (such as transitioning from Cryptomus to Heleket), and continue business as usual.
However, the coordinated enforcement demonstrated by the U.K. proves that modern blockchain intelligence—combined with aggressive, cross-border economic sanctions—can successfully pierce the veil of shell corporations and phantom regulators. By legally cutting off access to mainstream financial ecosystems and penalizing any entity that touches their liquidity pools, international regulators have fundamentally altered the risk calculus for cybercrime payment processors.
As blockchain forensics firms continue to map out secondary evasion networks, the downfall of Cryptomus serves as a stark warning to the underground digital economy: chameleonic payment platforms can change their names and hide behind fake regulators in disputed territories, but they can no longer outrun the reach of coordinated global sanctions.