Executive Overview
In a dramatic escalation of an ongoing international cybercrime investigation, federal law enforcement agents have arrested Edward Dubrovsky, the co-founder of prominent Canadian cybersecurity and ransomware advisory firm Cypfer. Dubrovsky was taken into custody in Pennsylvania in connection with an intensifying, multi-jurisdictional probe into the notorious ShinyHunters hacking collective.
The arrest comes on the heels of one of the most humiliating breaches in the history of American law enforcement: a cyberattack executed by ShinyHunters that successfully relieved the Federal Bureau of Investigation (FBI) of sensitive personnel data encompassing thousands of agents. The stolen cache reportedly includes granular details regarding unit assignments, specific specializations, and confidential medical and psychiatric records.
While initial mainstream reports, including coverage by The New York Times, remained vague regarding the identity of the detained individual, multiple investigative sources confirmed to KrebsOnSecurity that the man in custody is Dubrovsky—a veteran incident response expert, author of Cyber Extortion Strategic Response, and a prominent figure in the global cyber insurance and extortion negotiation ecosystem.
Federal court records indicate that Dubrovsky faces serious charges including cyber extortion and conspiracy. The case has already been transferred to the U.S. District Court for the Eastern District of Texas, which sources indicate has become the centralized command center for the entire federal inquiry into ShinyHunters. As law enforcement officers comb through seized digital assets and close the net on international cyber actors, the arrest of a senior incident response executive sends shockwaves through the cybersecurity industry, blurring the lines between corporate defense and illicit facilitation.
Detailed Chronology: From Philadelphia Summit to Federal Custody
The Trap Springs in Philadelphia
The sequence of events leading to Dubrovsky’s arrest began in early October 2026 during the annual Cyber Risk Summit held at the Loews Philadelphia Hotel from October 5 to October 7. Hosted by NetDiligence, the high-profile conference brought together elite figures from the cyber insurance, legal, and incident response sectors.
According to conference materials and public professional registries, Cypfer—the Canadian security firm co-founded by Dubrovsky—served as the summit’s premier sponsor. Dubrovsky, who had recently transitioned his professional focus to another security and advisory entity known as CyberSteward, had expressed anticipation on social media regarding his attendance at the event to discuss global, platform-agnostic strategies for handling coercive cyber extortion and ransomware settlement services.
Instead of networking with peers and insurance underwriters, Dubrovsky was intercepted by FBI agents. Federal court records confirm that an individual bearing his name—spelled "Edward Dobrovsky" in initial docket entries—was taken into custody on October 8.

Centralizing the Probe in Texas
Following his apprehension, Dubrovsky was initially booked and held at a federal facility in Philadelphia, with the U.S. Bureau of Prisons inmate locator confirming his detention. However, administrative court actions filed on October 9 reveal that the case was swiftly transferred to the Eastern District of Texas.
Legal analysts note that transferring venue to Texas points to a coordinated prosecutorial strategy. Sources close to the investigation indicate that the Eastern District of Texas has been designated as the central repository and command center for all legal proceedings, grand jury indictments, and evidentiary reviews tied to the ShinyHunters syndicate. The FBI has thus far declined to issue an extensive public comment regarding the precise nature of Dubrovsky’s alleged complicity, though the speed and scale of the transfer underscore the gravity of the federal case.
Supporting Context & Metrics: The Mechanics of ShinyHunters and the Extortion Ecosystem
Who is ShinyHunters?
To understand the significance of the FBI’s targeting of a ransomware negotiation executive, one must examine the operational footprint of ShinyHunters. The collective has established itself as one of the most prolific and disruptive cyber extortion syndicates operating globally.
- Modus Operandi: ShinyHunters routinely leverage sophisticated phishing campaigns and stolen corporate credentials to compromise software-as-a-service (SaaS) providers and enterprise cloud environments.
- Data Exfiltration and Extortion: Once inside a network, the group siphons massive volumes of proprietary and sensitive data, threatening to dump the files publicly on dark web forums or leak sites unless exorbitant ransom demands are satisfied.
- Financial Impact: According to federal estimates and incident metrics released by law enforcement agencies, ShinyHunters has successfully extorted upward of $70 million from corporate and institutional victims globally over the course of the year.
The Anatomy of the FBI Breach
The pressure on federal law enforcement intensified exponentially following a brazen retaliatory strike by the hackers. Immediately following the September arrest of reformed hacker-turned-cybercriminal Pepijn van der Stap by Dutch police—an operation heavily supported by international intelligence sharing—ShinyHunters underwent a leadership shift.
An operative operating under the handle "Rey" assumed tactical control of the group. Emboldened, Rey began openly taunting the FBI on social media and encrypted channels after successfully breaching the bureau’s own online recruitment portal. The stolen data trove included:
- Comprehensive personnel rosters containing unit assignments and operational specializations.
- Highly sensitive personal documentation, including background check files and confidential medical and psychiatric records of active-duty agents.
Subsequent journalistic reporting by Reuters revealed that "Rey" was actually a teenager named Saif Al-din Khader. Khader was successfully detained and is reportedly cooperating with federal investigators. Court filings and investigative reports highlight that Khader’s apprehension occurred precisely as the group was attempting to execute an extortion campaign against a major navigation and digital aviation unit recently divested by Boeing in late 2025.
The Paradox of Cyber Extortion Advisory
Edward Dubrovsky’s arrest introduces a troubling dynamic into the multi-billion-dollar incident response industry. Dubrovsky is not a traditional malware author or access broker; he is a recognized authority on the legal, strategic, and tactical realities of ransomware negotiations.

As the author of the 252-page industry text Cyber Extortion Strategic Response, Dubrovsky explicitly wrote about the nuances of dealing with cybercriminals. A widely cited excerpt from his book highlights a central tenet of modern incident response:
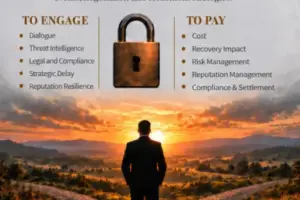
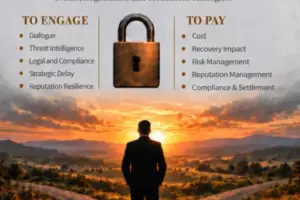
"At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
However, federal investigators are increasingly scrutinizing whether certain advisory and negotiation firms cross the legal threshold—transforming from authorized negotiators acting on behalf of distressed victims into entities that facilitate illegal extortion payments, potentially violating federal sanctions, anti-money laundering statutes, or aiding and abetting extortion conspiracies.
Official Statements and Industry Reactions
The federal government has maintained a guarded posture regarding the specifics of the ongoing investigation.
- FBI Leadership: FBI Director Kash Patel acknowledged the ongoing crackdown via social media statements following coordinated raids and arrests, though initial announcements omitted specific naming conventions prior to court docketing. The bureau has formally declined to elaborate on pending indictments.
- Legal Representation: Public records indicate that as of the initial court appearances, Dubrovsky has not retained private defense counsel, nor has the court formally appointed a public defender to manage his defense.
- Corporate Silence: Representatives for Cypfer and CyberSteward have faced mounting media inquiries. Despite public marketing footprints and previous speaking engagements at major cybersecurity summits, executives at these associated entities have largely declined immediate comment as legal teams scramble to assess the implications of the federal indictment.
Future Outlook: A Turning Point for Incident Response
The arrest of Edward Dubrovsky marks a watershed moment for the global cybersecurity community. For years, the multi-billion-dollar ecosystem surrounding ransomware negotiations has operated in a legal and regulatory gray area. Insurance carriers, corporate boards, and incident response firms routinely coordinate payouts to criminal enterprises to minimize operational downtime and prevent catastrophic data leaks.
As the dust settles on the Eastern District of Texas docket, industry experts anticipate several cascading effects:
- Heightened Regulatory Scrutiny: Regulatory bodies and federal prosecutors are expected to increase oversight on incident response firms, scrutinizing financial flows, cryptocurrency tracking, and communication channels between negotiators and known threat actors.
- Additional Indictments Expected: Sources close to the investigation have signaled that Dubrovsky may not be the last executive from the ransomware advisory sector to face federal scrutiny. Investigators are reportedly poring over digital devices seized during the Pepijn van der Stap raid in the Netherlands, looking for evidence of systemic cross-border coordination with cybercrime syndicates.
- Operational Paralysis in Extortion Defense: The chilling effect of prosecuting a prominent author and negotiation strategist will likely force corporate legal departments and cyber insurance providers to re-evaluate their risk tolerance when engaging third-party advisory firms.
As this fast-moving story continues to develop, investigators and legal scholars alike will be watching to see how the judiciary defines the boundary between lawful incident mitigation and criminal conspiracy in the high-stakes arena of cyber extortion.