In a stunning escalation of an already high-stakes international cybercrime investigation, federal law enforcement agents have arrested a high-profile Canadian cybersecurity executive in Pennsylvania. The arrest is directly tied to an ongoing, multi-jurisdictional crackdown on ShinyHunters, a notorious cybercriminal syndicate that recently managed to breach federal systems and siphon sensitive personal and professional data concerning thousands of Federal Bureau of Investigation (FBI) personnel.
The suspect, identified in federal court records as 54-year-old Edward Dubrovsky—an executive associated with the Canadian security firm CyberSteward and formerly with Cypfer—was taken into custody by FBI agents on October 8, 2026. Dubrovsky’s arrest occurred while he was visiting Philadelphia to attend the annual Cyber Risk Summit, a prominent gathering for cyber insurance and risk management professionals.
Federal court filings show that Dubrovsky has been charged with cyber extortion and conspiracy. Specifically, the preliminary criminal complaint charges the defendant with "conspiracy to threaten to impair the confidentiality of information with the intent to extort money" and "interference with commerce by threats." Although several core documents associated with the case remain sealed, the proceedings have already been transferred to the Eastern District of Texas, which sources close to the investigation indicate has become the central command hub for the overarching federal probe into ShinyHunters.
The arrest of a prominent figure within the ransomware negotiation and incident response industry marks a profound and troubling convergence between the legitimate cyber defense sector and the shadowy underworld of digital extortion. As federal authorities comb through seized digital assets and interrogate key figures across multiple continents, this developing scandal threatens to shake public trust in the commercial cyber defense ecosystem to its very core.
Detailed Chronology: From Philadelphia Conference to Federal Custody
To understand how a prominent Canadian cybersecurity leader became ensnared in a federal extortion probe, it is necessary to examine the rapid sequence of events that unfolded in early October 2026.
October 5 – October 7, 2026: The Cyber Risk Summit
The Loews Philadelphia Hotel played host to the NetDiligence Cyber Risk Summit, a major industry conference drawing insurance executives, legal experts, and incident response specialists from around the globe. Among the most prominent corporate sponsors of the event was Cypfer, a Canadian cybersecurity firm specializing in ransomware mitigation and extortion advisory services.
Edward Dubrovsky, a veteran figure in the Canadian cybersecurity landscape and the author of the 252-page textbook Cyber Extortion Strategic Response, had publicly announced via LinkedIn roughly a month prior that he would be attending the summit alongside members of his new team at CyberSteward. Little did attendees know that federal law enforcement was closing in on Dubrovsky, who allegedly maintained deeper ties to the criminal ecosystem than his public profile as a defender suggested.
October 8, 2026: The Arrest
On Wednesday, October 8, FBI agents moved in to arrest Dubrovsky in Pennsylvania. Court records indicate that an individual under the name "Edward Dobrovsky"—with a slight misspelling of his surname—was formally charged with conspiracy and cyber extortion. Following his apprehension, Dubrovsky was initially booked into a federal detention facility in Philadelphia, as logged by the U.S. Bureau of Prisons inmate locator.
October 9, 2026: Case Reassignment and Public Disclosures
The investigation shifted gears dramatically on October 9. Court records reveal that a legal notice was filed moving Dubrovsky’s case file directly to the U.S. District Court for the Eastern District of Texas. This transfer aligns with intelligence from multiple sources indicating that the Eastern District of Texas has assumed centralized control over the entire, sprawling ShinyHunters investigation.

Concurrently, mainstream media outlets, including The New York Times, began reporting on the arrest of an unidentified Canadian man in Pennsylvania linked to the ShinyHunters probe. Shortly thereafter, the identity of the suspect leaked through legal databases and investigative reporting by security journalist Brian Krebs, confirming Dubrovsky’s detainment.
As of press time, Dubrovsky remains unrepresented by formal legal counsel, with the courts yet to formally appoint a public defender. Cypfer, his former employer, issued a clarifying statement on October 10 noting that Dubrovsky was never a founder or co-founder of the firm—contrary to claims on his LinkedIn profile—but rather served as a managing director prior to his resignation in November 2025.
Supporting Context & Metrics: The Anatomy of the ShinyHunters Threat
The charges against Dubrovsky do not exist in a vacuum; they represent the latest seismic shockwave in an aggressive federal offensive against ShinyHunters, one of the most prolific and destructive data-theft syndicates operating in the global threat landscape.
Modus Operandi and Financial Impact
ShinyHunters typically targets Software-as-a-Service (SaaS) providers and corporate entities through sophisticated phishing campaigns and stolen credential harvesting. Once inside a victim’s network, the group exfiltrates massive volumes of proprietary and consumer data, threatening to leak the stolen assets publicly on extortion forums unless a ransom demand is satisfied.
According to internal FBI tracking metrics, ShinyHunters has successfully extorted more than $70 million from corporate victims globally over the course of 2025 and 2026 alone. Their operations have targeted organizations across diverse sectors, including aviation, technology, and financial services.
The Breach of the FBI
The urgency of the federal response intensified dramatically after ShinyHunters executed a devastating cyberattack against the FBI itself. The syndicate infiltrated the bureau’s online recruitment portal, relieving federal authorities of sensitive dossiers detailing thousands of active and prospective agents.
According to digital forensics and investigative findings, the stolen cache included:
- Detailed personnel rosters outlining specific bureau units and operational specializations.
- Highly confidential medical histories.
- Intimate psychiatric evaluation records of federal law enforcement personnel.
The compromise of internal FBI human capital data dealt a severe blow to the agency’s operational security, transforming the pursuit of ShinyHunters from a standard white-collar cybercrime investigation into a top-priority national security manhunt.
International Arrests and Global Sweep
Dubrovsky’s arrest is part of a broader, coordinated international crackdown on the infrastructure supporting ShinyHunters. Key milestones in this global campaign include:

- The Netherlands (September 2026): Dutch law enforcement authorities arrested Pepijn van der Stap, a reformed hacker suspected of playing a critical structural role within the ShinyHunters enterprise. Federal investigators immediately seized and began poring over electronic devices recovered during Van der Stap’s apprehension.
- The "Rey" Detainment (October 2026): Following Van der Stap’s arrest, a high-profile cybercriminal operating under the alias "Rey" assumed control of the ShinyHunters group. Rey began openly taunting FBI leadership on social media regarding the bureau data breach. Investigative reporting by Reuters and security researchers identified "Rey" as a teenager named Saif Al-din Khader. Khader was subsequently detained and is reportedly cooperating with federal investigators. His apprehension occurred as the group attempted to extort a digital aviation and navigation unit recently divested by Boeing in late 2025.
Official Statements and Industry Fallout
The arrest of a prominent incident response executive has sent shockwaves through the cybersecurity community, blurring the ethical and legal boundaries that govern the multi-million-dollar ransomware negotiation industry.
Official Silence and Cautious Communications
Thus far, official commentary from federal law enforcement leadership has been measured. FBI Director Kash Patel acknowledged the ongoing crackdown via a statement on X (formerly Twitter), celebrating the progress of the bureau’s cyber division without explicitly naming individual suspects. When approached for comment regarding Edward Dubrovsky’s specific role and corporate affiliations, FBI spokespersons declined to provide on-the-record statements, citing the ongoing and expanding nature of the federal grand jury investigation.
The Paradox of the "Ransomware Negotiator"
Dubrovsky’s arrest forces a harsh spotlight onto the specialized niche of cyber extortion advisory services. As the author of Cyber Extortion Strategic Response, Dubrovsky frequently lectured and wrote on the fine art of managing threat actors during corporate crises.
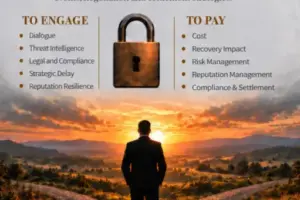
A central thesis of his published work—and a standard mantra within the professional negotiation industry—draws a sharp distinction between communication and capitulation:
"At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay," Dubrovsky wrote in promotional excerpts for his book. "Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
However, federal prosecutors in the Eastern District of Texas appear to believe that Dubrovsky’s activities crossed the legal line dividing legitimate advisory work from active criminal conspiracy, facilitation, or the illegal handling of extortion funds. As regulatory scrutiny tightens on ransomware intermediaries—who frequently handle cryptocurrency payments to unblock corporate networks—cybersecurity firms are hurriedly auditing their internal compliance programs, legal structures, and communications with known threat groups.
Future Outlook: What Lies Ahead for the Investigation
As federal investigators sift through the terabytes of data seized from Dutch servers, cooperative informants like Saif Al-din Khader, and the electronic devices of newly arrested executives, legal and cyber experts agree that this case is far from over.
- More Arrests Expected: Law enforcement sources indicate that the investigation into ShinyHunters and its broader network of facilitators is accelerating. Additional criminal charges against principals at other firms specializing in ransomware negotiation and incident response are widely anticipated in the coming weeks.
- Regulatory Crackdown on Extortion Advisories: The arrest of a prominent industry author and executive will likely prompt federal regulators and lawmakers to introduce stricter oversight, licensing requirements, and compliance mandates for private companies operating in the cyber insurance and ransomware negotiation space.
- The Fate of the Eastern District Prosecution: As the case proceeds in Texas, defense attorneys will undoubtedly challenge the legality of federal overreach into what may have been standard incident response protocols. Conversely, the Department of Justice appears determined to establish a hardline precedent demonstrating that aiding cyber extortion syndicates—regardless of corporate title or professional standing—will be met with severe criminal prosecution.
This is a rapidly evolving investigative story. Further updates, legal filings, and institutional statements will be published as additional details emerge from federal court proceedings.