Executive Overview
In a decisive move targeting the financial lifeblood of the Russian wartime economy and transnational cybercrime, the United Kingdom has unleashed sweeping economic sanctions against Cryptomus. Operating under a revolving door of corporate aliases—including Certa Payments, Xeltox Enterprises, and its most recent iteration, Heleket—Cryptomus has spent years functioning as a critical, chameleonic payment conduit. According to international blockchain forensics experts and intelligence analysts, the platform has actively facilitated billions of dollars in illicit transactions, serving as the financial engine room for ransomware gangs, narcotics syndicates, darknet markets, and high-tech fraud services.
Announced on October 8, the U.K. Treasury’s sanctions represent a watershed moment in international financial enforcement. The penalties legally freeze any assets held by Cryptomus within British financial institutions, while comprehensively barring U.K. companies and individuals from conducting any business operations with the platform, virtual or otherwise. Alongside Cryptomus, the British government cast its regulatory net wide, targeting fellow virtual payment networks VexPay, TokenSpot, and the Tsunami Payments service, which have similarly acted as bypass valves around Western financial restrictions.
While previous regulatory actions—most notably a record-shattering CAD $176 million fine levied by Canada in late 2025—inflicted financial penalties, industry experts emphasize that fines are easily ignored or evaded by borderless digital asset enterprises. By contrast, asset freezes and statutory commercial bans strike at the operational core of these networks. This enforcement action is also notable as the first known instance of a "Five Eyes" intelligence-sharing nation (comprising Australia, Canada, New Zealand, the United Kingdom, and the United States) directly sanctioning a cryptocurrency operation deeply rooted within another Five Eyes jurisdiction.
Underpinning Cryptomus is a bizarre web of shell corporations, fabricated regulatory bodies tied to disputed territories in northwest Africa, and a sophisticated strategy of regulatory arbitrage. As Western law enforcement agencies tighten the noose, the case of Cryptomus offers an unvarnished look at how modern cybercrime syndicates and sanctioned nation-states exploit the shadows of the global financial architecture.
Detailed Chronology: From Certa Payments to Heleket
The operational timeline of Cryptomus reveals a calculated game of corporate hide-and-seek, designed to outpace investigators, evade regulatory fines, and preserve an uninterrupted flow of illicit capital.
Emergence and Early Growth (2022–2024)
Emerging on the digital landscape in 2022 under the corporate banner of Certa Payments (and alternatively registered as Xeltox Enterprises), Cryptomus quickly positioned itself as a go-to merchant of anonymity for illicit enterprises. Operating out of a heavily shared office space in Vancouver—an address famously registered to dozens of other foreign currency dealers and money transfer businesses, none of which maintained a physical presence there—the platform quietly integrated itself into the Russian digital economy.
By late 2024, investigative reports by security journalists and blockchain analytics firms exposed Cryptomus as a primary payment processor for dozens of Russian cryptocurrency exchanges and underground websites hawking specialized cybercrime tools. During this foundational period, the platform handled vast sums of money with minimal oversight, relying on relaxed "Know Your Customer" (KYC) protocols to onboard high-risk clientele.
The Canadian Crackdown and the Birth of Heleket (2025)
As the transactional volume of Cryptomus swelled into the billions, international scrutiny intensified. In late 2025, Canadian regulatory authorities dropped a historic hammer on the platform, issuing a CAD $176 million administrative monetary penalty for severe, systemic anti-money laundering (AML) violations.
Faced with a crippling nine-figure fine, Cryptomus executed a classic evasion maneuver: it formally appealed the penalty while simultaneously launching a parallel service named Heleket. While the original Cryptomus platform briefly instituted stricter KYC requirements—causing a temporary dip in transaction metrics—Heleket stepped seamlessly into the void. Heleket immediately began operating as an uninhibited, no-KYC payment processor, absorbing the overflow of high-risk clients, ransomware operators, and darknet vendors who refused to submit to identity verification.
When intelligence analysts and investigators attempted to probe Heleket’s corporate governance, its Telegram-based support agents brazenly claimed—despite glaring forensic overlaps and shared infrastructural DNA—that Heleket maintained zero corporate affiliation with Cryptomus.
The U.K. Hammer Drops (October 2026)
The cat-and-mouse game reached a definitive turning point on October 8, 2026. Recognizing that administrative fines imposed by countries like Canada were ultimately uncollectible and toothless against a digital enterprise operating without physical footprints, the United Kingdom stepped in with full economic sanctions.

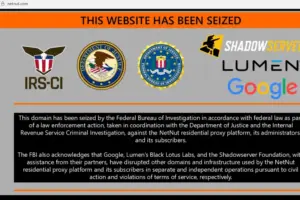
The immediate operational impact was swift. On the day the sanctions went live, users attempting to route funds through the platform’s Telegram bots were greeted by automated error messages stating that the systems were abruptly unable to process transactions. Within hours, the digital infrastructure underpinning Cryptomus and its spin-offs began to fray under the weight of coordinated international blacklisting.
Supporting Context & Metrics: The Scale of the Illicit Pipeline
To fully grasp the threat posed by Cryptomus, one must examine the staggering volumes of capital that coursed through its digital veins. Blockchain intelligence firms have spent years mapping the financial flows, revealing an industrial-scale laundering operation that far outpaced traditional underground financial mixing services.
Tracing the Billions
In April 2026, leading blockchain analysis firm TRM Labs published a comprehensive threat intelligence dossier on Cryptomus. The findings were staggering: since its inception in 2022, the platform had processed more than $7 billion in cumulative transactions. This enormous sum was not merely the product of legitimate e-commerce; TRM Labs’ tracing identified direct connections to some of the darkest corners of the internet, including:
- Vendors trafficking in Child Sexual Abuse Material (CSAM).
- State-aligned and independent terrorist financing networks.
- Transnational human trafficking operations.
- Ransomware syndicates extracting extortion payments from Western hospitals, critical infrastructure, and Fortune 500 corporations.
The Chainalysis Data: Outpacing Traditional Mixers
According to a detailed October 8, 2026, advisory published by Chainalysis, Cryptomus and its successor, Heleket, evolved into structural pillars of the wartime Russian economy, helping entities bypass strict Western financial sanctions.
"Cryptomus and Heleket have emerged as major payment hubs for illicit activity," Chainalysis noted in their analytical blog post. "Together, these services received more illicit funds across tracked categories than the mixers in our dataset, and the number of illicit counterparties surged to more than 900 in a single month in late 2025."
This metric is particularly telling. Cryptocurrency "mixers"—such as the notorious Tornado Cash—were long considered the gold standard for obfuscating illicit digital funds. For a single commercial payment processor to eclipse the volume of dedicated mixers underscores how platforms like Cryptomus weaponized pseudo-legitimate merchant services to launder criminal proceeds at scale.
Official Statements and Forensic Insights
The dismantling of Cryptomus has been propelled by a tight-knit coalition of independent blockchain investigators and corporate intelligence giants. Their insights illuminate the mechanics of how modern cybercrime infrastructure operates in plain sight.
The Distinction Between Fines and Sanctions
Richard Sanders, a veteran blockchain analyst and investigator who spent months mapping Cryptomus’s intricate payment pathways and transacting undercover with its customers, was quick to highlight why the U.K. sanctions are uniquely lethal compared to previous regulatory actions.
Writing on professional networks following the announcement, Sanders cut straight to the heart of the matter:
"A fine doesn’t stop a cryptocurrency payment processor from processing payments. Sanctions kill the operation. The distinction matters."
Sanders noted that Canada’s monumental CAD $176 million fine, while impressive on paper, was fundamentally unenforceable. Cryptomus simply absorbed the financial penalty as a cost of doing business, appealed the ruling in domestic courts, spun up Heleket as an operational duplicate, and continued business as usual. It required the sovereign muscle of British economic sanctions—with their extraterritorial enforcement capabilities and banking prohibitions—to deliver a near-fatal blow to the enterprise.

The Geopolitical Milestone
Furthermore, Sanders pointed out the profound geopolitical significance of the U.K. action. For the first time within the intelligence-sharing framework of the "Five Eyes" alliance, one member state has actively sanctioned a corporate entity incorporated within the borders of a fellow member state. This breaches traditional jurisdictional hesitations, signaling that Western allies are increasingly willing to step on each other’s toes to neutralize systemic national security threats hiding behind corporate charters in allied nations.
The Phantom Regulator: Tracing the Roots to Western Sahara
Perhaps the most bizarre and illuminating aspect of the Cryptomus investigation lies in how the platform legitimized its operations. Where do illicit digital currency exchanges and high-risk payment processors derive their authority to operate? In the case of Cryptomus, the answer reads like a geopolitical thriller involving phantom regulators and disputed territories.
The Ukrainian Connection and Phony Authorities
Investigative deep dives into the corporate registry documents of Certa Payments (Cryptomus’s parent company) revealed that its sole shareholder was a 25-year-old Ukrainian national. Alongside her role at Certa Payments, this individual also headed several other distinct corporate entities, most notably the WS Management and Advisory Corporation.
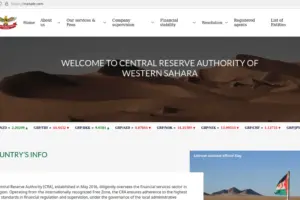
WS Management and Advisory Corporation marketed itself aggressively online as an exclusive, authoritative regulatory body. Its stated mission? To issue official licenses for cryptocurrency operations, foreign exchange (forex) brokers, and online gaming businesses seeking incorporation within the Western Sahara—a disputed region in northwest Africa that lacks widespread international recognition as a sovereign nation.
The CRASADR Ecosystem
The primary digital storefront for this regulatory apparatus was hosted at crasadr.com, the official portal of the Central Reserve Authority of Western Sahara. This remarkably brazen website purported to oversee the legal licensing of financial institutions, providing applicants with turnkey corporate formation packages and assistance in setting up correspondent bank accounts.
Forensic web mapping by investigators uncovered deep digital footprints connecting these entities. For instance, an early primary domain utilized by Certa Payments (certa.website) shared a physical server infrastructure with 12 distinct domains. Among them was rasd-state.ws, a direct node used by the Central Reserve Authority of Western Sahara to publish lists of approved cryptocurrency and gaming entities.
This web of phantom oversight demonstrates a dangerous new frontier in cybercrime: the creation of synthetic sovereign jurisdictions. By leveraging unrecognized territories or disputed geopolitical zones, illicit payment processors can manufacture "legal" compliance frameworks out of thin air, issuing themselves licenses that satisfy rudimentary compliance checks while remaining entirely detached from legitimate international law.
Future Outlook: The Crackdown on Crypto Arbitrage
The U.K.’s decisive action against Cryptomus and Heleket marks a critical turning point in the global campaign to sanitize the cryptocurrency ecosystem and choke off financial lifelines to sanctioned regimes. However, the saga also lays bare the enduring resilience of transnational cybercrime networks.
As enforcement agencies close the net on platforms like Cryptomus, TokenSpot, and VexPay, the architects of these illicit payment rails are already adapting. Security analysts predict that future iterations of underground payment processors will rely increasingly on decentralized protocols, peer-to-peer (P2P) fiat-to-crypto bridging, and multi-layered artificial intelligence to evade blockchain analytics tracing.
Nevertheless, the U.K. sanctions send an unmistakable warning flare to the broader digital asset industry. The era of regulatory safe havens—where shell companies can hide behind fake foreign regulators in disputed territories while funneling billions for ransomware gangs and Russian state interests—is rapidly drawing to a close. For compliance officers, traditional financial institutions, and cryptocurrency exchanges alike, the message is clear: interacting with chameleonic payment processors like Cryptomus is no longer just a regulatory compliance risk; it is an invitation to direct legal annihilation.