Executive Overview
In a decisive escalation against transnational cybercrime and the financial infrastructure fueling Russia’s wartime economy, the United Kingdom has issued sweeping economic sanctions against Cryptomus. Known for its ability to rapidly morph its corporate identity and evade regulatory crackdowns, Cryptomus is described by blockchain intelligence experts as a major global conduit for illicit funds. The platform has routinely funneled payments for ransomware gangs, narcotics rings, darknet marketplaces, fraud operations, and specialized cybercrime services designed to help Russian entities circumvent international financial restrictions.
Announced on October 8, the U.K. Treasury’s sanctions freeze any assets held by Cryptomus within British financial institutions and legally prohibit UK-based companies and citizens from conducting any business, virtual or otherwise, with the platform. Alongside Cryptomus, the U.K. government targeted several other affiliated virtual payment rails, including VexPay, TokenSpot, and the Tsunami Payments service.
These sanctions mark a watershed moment in international cryptocurrency enforcement. Notably, they represent the first time a member of the "Five Eyes" intelligence-sharing alliance (Australia, Canada, New Zealand, the United Kingdom, and the United States) has formally sanctioned a major crypto operation originally incorporated within another Five Eyes jurisdiction. Furthermore, cybersecurity experts emphasize that while administrative penalties and multi-million-dollar fines—such as those previously levied by Canada—can often be sidestepped or ignored by shadowy digital entities, sovereign economic sanctions deal a crippling, operational blow.
Detailed Chronology of an Illicit Empire
The trajectory of Cryptomus from an obscure startup to a multi-billion-dollar illicit payment processor illustrates the profound challenges law enforcement faces in policing decentralized digital assets.
Emergence and Early Growth (2022–2023)
Cryptomus emerged on the digital landscape in 2022, operating initially under corporate names such as Certa Payments and Xeltox Enterprises, while maintaining a nominal corporate address in Vancouver, Canada. Despite listing a physical headquarters in British Columbia, investigations revealed that this address was shared with dozens of other foreign currency dealers and money transfer businesses—none of which appeared to have a genuine physical presence at the location.
From its inception, the platform positioned itself as a business-friendly crypto payment gateway. However, behind its polished facade, Cryptomus quickly became the payment processor of choice for a sprawling ecosystem of Russian cryptocurrency exchanges and underground websites hawking cybercrime-as-a-service infrastructure.
The Canadian Crackdown and the Pivot to "Heleket" (2024–2025)
As investigative journalists and blockchain analysts began peeling back the layers of the platform, the sheer volume of illicit transactions routed through Cryptomus drew the attention of regulators. In December 2024, investigative reports detailed how Cryptomus served as the crucial bridge converting cryptocurrency into fiat cash within Russian banking networks.
Faced with mounting evidence of compliance failures, Canadian authorities launched an investigation that culminated in October 2025, when Canada slapped Cryptomus with a record-shattering CAD $176 million fine for severe anti-money laundering (AML) violations.
Rather than complying with regulatory mandates or paying the penalty, Cryptomus engaged in a classic chameleonic maneuver. The platform appealed the fine, dropped the "Cryptomus" moniker in favor of a parallel service dubbed Heleket, and continued to process massive volumes of high-risk transactions while openly flaunting no-KYC (Know Your Customer) policies. Support agents operating Heleket’s official Telegram channels brazenly denied any corporate affiliation with Cryptomus, even as blockchain tracing proved the infrastructure was identical.

The U.K. Hammer Drops (October 2026)
By late 2025 and into 2026, the evasion tactics could no longer shield the network from coordinated Western pressure. On October 8, 2026, the United Kingdom formally designated Cryptomus under its Russia sanctions regime. Within hours of the announcement, user support bots on Telegram began notifying panicked clients that the platform was abruptly unable to process transactions, effectively shuttering major operational arteries of the network.
Supporting Context, Metrics, and Scale of Abuse
The financial footprint of Cryptomus and its successor entities is staggering, illustrating how specialized payment processors operate as the lifeblood of the modern cybercrime economy.
Transaction Volumes and Illicit Exposure
According to data compiled by blockchain analysis firm TRM Labs in April 2026, Cryptomus processed more than $7 billion in cumulative transactions since its founding in 2022. TRM’s intelligence library revealed that this immense volume included funds directly linked to some of the most abhorrent digital crimes, including vendors of child sexual abuse material (CSAM), state-aligned terrorist financing networks, and international human trafficking operations.
Data from Chainalysis, published in conjunction with the U.K. sanctions announcement, further underscored the systemic nature of the threat. Chainalysis reported that Cryptomus and Heleket emerged as dominant hubs for illicit activity, noting that:
- Surpassing Mixers: The services received more illicit funds across tracked categories than traditional cryptocurrency mixing services in the dataset.
- Explosive Growth in Counterparties: The number of illicit counterparties interacting with the network surged past 900 in a single month in late 2025.
TRM Labs also noted an interesting operational shift: when Cryptomus briefly experimented with implementing stricter KYC verification rules, its overall transaction volume cratered. Realizing that compliance was toxic to its core customer base, the operators abandoned the experiment and launched Heleket as a dedicated, unverified payment channel to recapture illicit market share.
Official Statements and Industry Analysis
The international response to the Cryptomus network highlights a growing consensus among blockchain analytics firms and geopolitical strategists: traditional monetary fines are insufficient against borderless crypto syndicates, but targeted sanctions provide a lethal blow.
The Distinction Between Fines and Sanctions
Richard Sanders, a veteran blockchain analyst and investigator who spent months mapping Cryptomus’s intricate payment infrastructure and interacting directly with its customer service portals, emphasized why the U.K. action represents a turning point.
"A fine doesn’t stop a cryptocurrency payment processor from processing payments," Sanders wrote in a public analysis. "Sanctions kill the operation. The distinction matters."
Sanders noted that Canada’s landmark CAD $176 million fine, while historic in monetary terms, was ultimately uncollectible and unenforceable given the shell-company structure of the enterprise. By contrast, the U.K. sanctions criminalize any interaction with the platform, severing its access to legitimate liquidity and forcing international payment partners to sever ties immediately.

Chainalysis on Wartime Evasion
In its official advisory, Chainalysis stressed that the actions against Cryptomus and TokenSpot are part of a broader, necessary campaign to dismantle the financial scaffolding supporting the Russian state.
"Cryptomus and Heleket have emerged as major payment hubs for illicit activity," Chainalysis stated. "Targeting these nodes is vital to disrupting the infrastructure that enables sanctioned Russian entities to bypass international financial isolation."
The Anatomy of a Phantom Regulator
One of the most bizarre and illuminating aspects of the Cryptomus investigation is the shell game of legitimacy utilized by its creators. To project an aura of official oversight, the operators relied on a web of fake financial institutions overseen by a phony regulatory body rooted in a territory not globally recognized as a sovereign nation.
The Western Sahara Connection
An extensive 2024 investigation uncovered that the sole shareholder of Certa Payments (Cryptomus’s parent company) was a 25-year-old Ukrainian national. This individual simultaneously headed several other corporate entities, most notably the WS Management and Advisory Corporation.
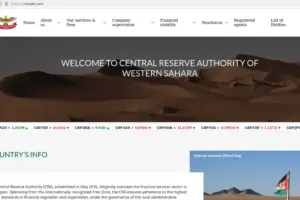
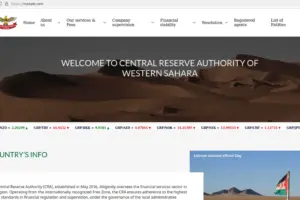
WS Management and Advisory Corporation aggressively marketed itself as an exclusive regulatory body responsible for issuing licenses to cryptocurrency exchanges, foreign exchange brokers, and online gaming platforms incorporated within the disputed region of Western Sahara in northwest Africa.
Operating through the website crasadr.com—purportedly the domain of the Central Reserve Authority of the Western Sahara—the fake regulator offered applicants illegitimate assurances of compliance, bank setup assistance, and official licensing. Technical analysis by investigators revealed that one of Certa Payments’ former domains (certa.website) shared a server with a dozen other suspicious domains, including rasd-state.ws, further unmasking the artificial paper trail constructed to deceive banking partners and compliance officers.
Future Outlook
The U.K. sanctions against Cryptomus and its sibling platforms signal a permanent shift in how Western governments approach decentralized financial crime. As nation-states increasingly rely on cybercrime proxies, ransomware extortion, and crypto-based sanctions evasion to fund geopolitical agendas, regulatory tolerance for "chameleonic" payment processors has evaporated.
However, the takedown of Cryptomus and Heleket will not eliminate the demand for clandestine payment rails. Security analysts warn that the architects behind these platforms are likely already preparing their next iteration—shifting jurisdictions, adopting new obfuscation technologies, and establishing fresh shell corporations behind fictional regulatory authorities.
The ultimate success of the U.K.’s intervention will depend on aggressive, cross-border enforcement, real-time blockchain surveillance, and the willingness of other Five Eyes allies to harmonize their legal frameworks. Until global law enforcement can seamlessly translate multi-million-dollar administrative penalties into enforceable asset seizures and criminal indictments across all digital jurisdictions, the game of corporate whack-a-mole between regulators and cybercrime-friendly crypto processors is bound to continue.