Executive Overview
In September 2026, the fragile intersection of international law enforcement, global corporate supply chains, and the subterranean economy of cybercrime was violently shaken. Authorities in the Netherlands arrested 24-year-old Pepijn van der Stap, a convicted cybercriminal known in underground forums by the handle “Umbreon.”
Van der Stap’s detention—stemming from suspicions that he aided the prolific, destructive hacker collective ShinyHunters—ignited an unprecedented chain reaction. Within days of his arrest, remaining members of ShinyHunters dramatically escalated their operations. They launched a brazen data-theft campaign targeting the job application portal of the Federal Bureau of Investigation (FBI) and aggressively extorted the Russian-speaking ransomware syndicate Cl0p.
Behind this sudden shift in tactics lies a toxic internal power struggle, cross-continental betrayals, and the alleged rise of a teenage mastermind from Amman, Jordan. What began as a local law enforcement sweep in the Netherlands has rapidly evolved into a global geopolitical and cybersecurity crisis, laying bare the volatile and unpredictable nature of modern criminal syndicates.
Detailed Chronology: From Almere to Global Cyber Warfare
The Dr. Jekyll and Mr. Hyde of Dutch Cybersecurity
The saga of Pepijn van der Stap is a textbook case of the modern dual-life cybercriminal. Based in Almere and Lelystad, van der Stap was convicted in late 2023 for a string of data thefts and extortions that prosecutors estimated yielded between €1.5 million and €2.7 million.
During his 2023 trial, van der Stap admitted to living a double life. By day, he worked as a software engineer at the Amsterdam-based cybersecurity startup Hadrian and volunteered for the Dutch Institute for Vulnerability Disclosure (DIVD), a nonprofit security research organization. By night, operating under the moniker “Umbreon,” he extorted victims and traded stolen databases on English-language hacking forums like RaidForums and Breached.
Van der Stap was sentenced to four years in prison (with one year suspended). Pleading ongoing psychological issues, including post-traumatic stress disorder (PTSD) stemming from childhood trauma, he initially opted to remain in custody to secure better treatment before eventually being released in December 2025.
In a September 2026 interview, van der Stap presented himself as a reformed individual attempting to make amends and rebuild his life, holding a position as an offensive security lead at the Dutch firm Neo Security. However, his public reformation mask cracked permanently mid-month.

The Arrest and the Escalation
According to sources familiar with the investigation, Dutch authorities detained van der Stap on or around September 16, 2026. Colleagues later reported witnessing police carting physical items out of his residence.
The Dutch police had been intensely tracking the infrastructure of ShinyHunters, particularly after an audio clip from February 2026 surfaced. In the recording, a native Dutch-speaking ShinyHunters member used social engineering to infiltrate Odido, the Netherlands’ largest mobile telecommunications provider. Tricking an employee into logging into a spoofed website, the hackers stole personal data belonging to over 6.2 million Dutch citizens.
When Dutch media publicized the audio, ShinyHunters aggressively confirmed the suspect was in their ranks, publicly mocking the Dutch police as "incompetent, irrelevant, unimportant, and useless" while promising severe retaliation if authorities attempted to interfere further.
Following van der Stap’s detention, that retaliation materialized with terrifying speed.
The FBI and Cl0p Breaches
Just days after van der Stap’s arrest, ShinyHunters claimed responsibility for an astonishing breach at apply.fbijobs.gov, the official job application portal for the FBI.
According to investigations by 404 Media and Reuters, the stolen data compromised the Social Security numbers and personal details of more than 5,000 FBI personnel. The compromised records included sensitive team assignments—such as special agents, threat intake examiners, and personnel tracking foreign state-sponsored cyber threats—as well as deeply personal medical and psychiatric evaluation files.
Concurrently, the syndicate targeted the Russian ransomware group Cl0p, executing extortion schemes against them and broadcasting taunting memes across social media.

Supporting Context & Metrics: The Mechanics of the Breach
The PeopleSoft Zero-Day and the WAF Bypass
How did a hacker collective breach some of the most heavily fortified networks on the planet? According to technical disclosures from Mandiant and the Google Threat Intelligence Group (GTIG), ShinyHunters leveraged a critical, newly patched vulnerability (CVE-2026-35273) in PeopleSoft, an enterprise SaaS platform managed by Oracle.
Initially exploited as a zero-day vulnerability in June 2026, Oracle hurried out a security patch, while Mandiant issued web application firewall (WAF) mitigation rules. However, in late September, security researchers reported that ShinyHunters circumvented these defenses entirely by deploying a sophisticated URL-encoding trick.
This technique enabled the mass exploitation of systems across a wide range of industries, including healthcare, higher education, technology, agriculture, transportation, and government agencies globally.
The Umbreon Signature and Internal Infighting
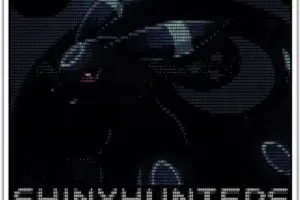
The FBI job site defacement left little doubt about the perpetrators’ theatrical flair. The hackers dropped an ASCII art design featuring the Pokémon character Umbreon alongside the mocking proclamation: "This site has been seized by ShinyHunters. rooting your systems since ’19 ;)."
This imagery served a dual purpose. According to intelligence sources, the oversized Umbreon graphic was an intentional plant by "Rey," a teenage cybercriminal from Amman, Jordan. Rey operates as a core administrator for ScatteredLapsussHunters (SLSH)—an amalgamation of three infamous hacking factions: Scattered Spider, LAPSUS$, and ShinyHunters.
Rey reportedly harbored deep animosity toward van der Stap over control of the ShinyHunters brand, data repositories, and financial spoils. By splashing the "Umbreon" alias across the defaced FBI portal, Rey sought to muddy the waters and actively pin the high-stakes federal breach squarely on the detained Dutchman.
Financial Realities and Scale
While van der Stap historically claimed his primary motivation was merely accumulating the world’s most comprehensive database ("My habit was collecting… collecting data, organizing data"), the modern ShinyHunters apparatus operates strictly as a high-stakes corporate extortion machine.

According to estimates shared by Mandiant researcher Austin Larsen, ShinyHunters’ aggressive multi-vector extortion spree has positioned the syndicate to pull in a staggering $100 million in extortion payments over the course of 2026 alone.
Official Statements and Judicial Developments
The international fallout prompted high-level responses from both European and American law enforcement agencies.
- Dutch Police Actions: Confirming the arrest of the 24-year-old suspect, the Dutch police announced that van der Stap was scheduled to appear before the Rotterdam District Court to face formal charges. In a shocking late development reported by the Dutch news outlet RTL, investigators revealed they are probing whether van der Stap attempted to orchestrate at least two contract murders overseas, indicating the criminal enterprise had crossed the line from data theft into physical violence.
- The FBI Response: Brett Leatherman, Assistant Director of the FBI’s Cyber Division, released a video statement explicitly addressing the ShinyHunters network. Leatherman thanked Dutch law enforcement partners and delivered a stark warning to the remaining members of the hacking group:
"Arrests have a way of changing who is willing to talk, and seized infrastructure has a way of showing us who’s left. The longer you stay in this, the more we learn about you. You know how to find us, and we know how to find you. I suggest you reach out to us while the choice is still yours."
Future Outlook
The arrest of Pepijn van der Stap and the subsequent aggressive lashing out by ShinyHunters under the leadership of Rey mark a critical turning point in the modern cyber threat landscape.
Several major implications define the road ahead:
- Erosion of Criminal Solidarity: The ease with which factions within SLSH and ShinyHunters betrayed one another—coupled with attempts to frame associates for high-profile federal crimes—signals that loyalty within elite cybercrime syndicates is virtually nonexistent. Law enforcement agencies are increasingly positioned to exploit these internal fractures.
- Hardening Enterprise Software Supply Chains: The weaponization of the Oracle PeopleSoft vulnerability underscores the systemic danger posed by enterprise HR and payroll platforms. As nation-states and criminal cartels alike weaponize zero-days against foundational business software, organizations will face mounting pressure to accelerate patch deployments and adopt zero-trust architectural models.
- The Escalation of Cross-Border Cyber Warfare: With the FBI’s personnel files compromised and Russian ransomware syndicates finding themselves on the receiving end of extortion, the boundaries between traditional financial cybercrime and geopolitical intelligence operations have blurred entirely.
As Dutch prosecutors prepare their case—now encompassing not only large-scale data theft and extortion, but potentially orchestrating violent crimes—the digital underworld watches anxiously. The fallout from the "Umbreon" arrest proves that while code can be obfuscated and servers can be hidden behind VPNs, the human elements of ego, greed, and betrayal remain a hacker’s ultimate undoing.