Executive Overview
In a landmark coordinated crackdown on global cybercrime, Google—working in tandem with a coalition of cybersecurity specialists, industry investigators, and the Motion Picture Association (MPA)—has successfully dismantled a massive, deeply entrenched botnet comprising more than 1.3 million pre-infected Android TV set-top boxes.
Dubbed XCPE by the Google Threat Intelligence Group (GTIG) after one of its core components, this sprawling cyber threat relied on hardware pre-loaded with covert malicious software straight from the factory floor. These compromised internet-connected devices secretly rented out innocent users’ residential broadband connections to global strangers while engaging in widespread advertising fraud and facilitating malicious web traffic.
According to forensic experts involved in the operation, the true scope of the infrastructure is significantly larger than the initial baseline figures suggest. The takedown actions are estimated to have severed access to upwards of 10 million additional compromised Internet of Things (IoT) ecosystems, ranging from Android-based healthcare and telehealth hardware to digital signage and karaoke machines.
The operation has exposed a dark underbelly in global hardware manufacturing and digital supply chains. By highlighting how Chinese original equipment manufacturers (OEMs) weaponized low-cost streaming devices, the takedown sheds light on the lucrative, multi-billion-dollar shadow economy of residential proxies, illicit streaming ecosystems, and digital ad fraud.
Detailed Chronology & Mechanics of the XCPE Threat
The Factory-Floor Infection Vector
The origins of the XCPE botnet trace back to Videostrong Technology Co., a China-based manufacturer of media streaming boxes. According to comprehensive technical disclosures by GTIG, Google officially severed all ties with Videostrong after investigators uncovered systematic, deliberate malicious code injection directly into the firmware of the devices before they ever reached store shelves or consumers’ living rooms.
Despite Google enforcing stringent compatibility and security protocols across Android device ecosystems to safeguard consumers, Videostrong engineered a way to execute malicious code the exact moment an end user booted up a newly purchased device for the very first time. Google has since patched the underlying operating system vulnerabilities that allowed this initial execution phase to occur, but the structural damage inflicted over the years serves as a stark warning regarding trust in global hardware supply chains.
Monetizing the Backdoor: Residential Proxies and Criminal Affiliates
Once activated within a user’s home network, the XCPE malware established clandestine backdoors to monetize the connection. GTIG’s investigative report notes that Videostrong deliberately transformed the hardware into a commercial asset by selling illicit access to criminal affiliates.
These affiliates loaded secondary modules onto the devices, turning the hardware into exit nodes for commercial residential proxy services. While residential proxies are legitimate tools used in some enterprise environments for web scraping or geo-testing, they are frequently exploited by malicious actors to anonymize cyberattacks, execute large-scale account takeover (ATO) campaigns, automate ad fraud, and scrape data to feed artificial intelligence (AI) models.
Expanding the Footprint: From MECOOL to Superbox
Parallel investigations by the cybersecurity startup Synthient—which collaborated closely with Hollywood’s Motion Picture Association—revealed that Videostrong’s malware extended far beyond generic white-label boxes. Synthient analyzed pre-infected streaming boxes sold under the MECOOL brand by Skyworth Technology, a publicly traded firm in China. The findings confirmed that MECOOL devices similarly bundled Videostrong’s malware payload.

This hardware-level infection model mirrored findings from late 2025, when researchers from Censys identified popular Superbox streaming boxes bundling residential proxy software like Grass.
These streaming boxes achieved massive commercial success through aggressive influencer marketing campaigns across TikTok, YouTube, and other major social networks. Content creators frequently pitched the devices as a cost-effective, one-time-fee alternative to mainstream cable, misleading consumers by granting access to hundreds of pirated pay-TV channels.
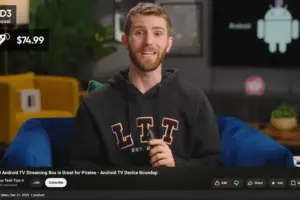
Notably, MECOOL hardware spiked in popularity following a 2023 endorsement by the massively popular YouTube channel Linus Tech Tips, which commands nearly 17 million subscribers. Following the unmasking of the threat, representatives for Linus Tech Tips confirmed they updated the original video to explicitly frame the product as a security risk and removed all associated affiliate monetization links.
Supporting Context & Metrics: The Global Proxy Ecosystem
The GTIG investigation mapped out the systemic integration of the XCPE botnet with numerous commercial residential proxy providers whose software development kits (SDKs) were weaponized by the underlying malware. The named entities span several prominent players in the proxy market:
- AppSalt / Honeygain: Developed by Vilnius, Lithuania-based Oxylabs. In late 2026, Oxylabs and Honeygain restructured under an umbrella entity named Source, following a $130 million funding injection from private equity giant Warburg Pincus that reportedly valued the enterprise at $3.6 billion.
- NetNut: Operated by the publicly traded Israeli company Alarum Technologies. In July 2026, the FBI and international industry partners seized hundreds of domains tied to NetNut, alleging the firm was behind a parallel TV box proxy botnet named Popa.
- Other Associated Providers: The GTIG report flagged additional proxy networks integrated into the infrastructure, including EarnFM, Traffmonetizer, Jaguar, LINKFOG, BMW/IPWeb, and GaGaNode.
The Broader Botnet Landscape: Kimwolf and Beyond
The XCPE takedown does not exist in a vacuum. Earlier in 2026, Synthient published groundbreaking research into the Kimwolf botnet, which had been hammering global networks with record-breaking Distributed Denial of Service (DDoS) attacks. Synthient demonstrated how Kimwolf rapidly infected millions of Android set-top boxes overnight, utilizing vulnerabilities within residential proxy frameworks to compromise other local network IoT devices—such as printers, smart home gadgets, and secondary media players.
Synthient’s public disclosures pressured multiple residential proxy networks to patch vulnerabilities, fragmenting Kimwolf into smaller, more manageable clusters. This intelligence eventually drew the attention of the Motion Picture Association, which stepped up efforts to purchase, dismantle, and reverse-engineer tainted streaming hardware.
Official Statements and Industry Responses
Google’s legal and technical interventions successfully dismantled the primary command-and-control (C2) domains and servers operated by Videostrong. In its published advisory, GTIG issued a blistering critique of the manufacturing sector:
"A device manufacturer intentionally infecting their users with malware is an unacceptable breach of trust, and represents a serious risk to those users. Without users’ knowledge or consent, infected devices were offered as a distribution mechanism for a wide array of criminal actors."
Ben Brundage, founder of Synthient, echoed these sentiments, characterizing the verified 1.3 million infection baseline as a "highly conservative" metric.

"The scale of affected devices is likely way higher," Brundage noted in an interview with security journalists. "This is probably the largest operation against backdoored TV boxes that we’ve seen."
The Proxy Providers Respond
Following the initial publication of these investigative findings, Oxylabs issued an official statement addressing how their infrastructure was exploited by the XCPE operators. While maintaining that their network design is intended to require explicit user consent before a node can operate as a proxy exit, the company admitted that malicious developers actively faked these verification signals.
"We have been conducting regular audits of the applications provided by our partners," the Oxylabs statement read. "However, following this incident, we will improve the application and application’s build fingerprinting logic to better detect cases where the SDK is running on an unapproved build of an originally authorized application."
Oxylabs clarified that they had no corporate record of a direct business relationship with Videostrong Technology Co., but confirmed they maintained ties with an upstream supplier utilizing the domain com.abc[.]nexus—identified by GTIG as an external malware loader.
"As soon as we saw that, we suspended the relationship and sent them a formal legal inquiry," Oxylabs added. "This supplier accounts for less than 1% of our IP address pool. We had a signed contract with them, they assured our QA team that users had given consent, and we saw the consent flow ourselves."
Future Outlook: Securing the IoT and Supply Chain
The dismantling of the XCPE botnet marks a monumental tactical victory for global cybersecurity defenders, cloud intelligence teams, and law enforcement agencies. However, security analysts warn that the underlying economic incentives driving these operations remain intact.
Because residential proxy networks command high market valuations—evidenced by multi-billion-dollar private equity investments in the sector—rogue developers and unscrupulous overseas hardware manufacturers will continue seeking out alternative vectors to monetize unsuspecting consumer bandwidth.
Moving forward, the fallout from the XCPE exposure is expected to trigger several structural shifts:
- Rethinking Android Device Certification: Major platform architects like Google are under mounting pressure to enforce continuous firmware integrity checks, ensuring that factory-installed images cannot be tampered with post-compilation without triggering automated security blocks.
- Scrutiny of Proxy SDK Integrations: Proxy network operators face increasing legal liabilities and mandatory technical audits to ensure that Software Development Kits embedded in third-party applications cannot be hijacked or illicitly cross-loaded onto unauthorized hardware.
- Consumer Awareness Regarding Gray-Market Streaming: Security advocates emphasize that "too-good-to-be-true" streaming boxes—frequently marketed via social media influencers offering lifetime access to pay-TV networks for a nominal flat fee—pose severe cyber hygiene risks. These devices are frequently subsidized by the illicit monetization of consumer broadband connections.
As collaborative intelligence sharing between tech giants, threat intelligence startups, and trade groups like the MPA continues to mature, cybercriminal syndicates will find it increasingly difficult to operate unchecked from the manufacturing floor to the consumer’s living room. Nevertheless, the XCPE incident remains a stark reminder that the security of a smart home network is only as strong as the integrity of the supply chain that built it.