In an alarming cybersecurity oversight, multiple White House staffers have inadvertently transformed government-issued and personal devices within the Executive Office of the President into commercial proxy nodes. Security researchers have revealed that computers and mobile devices connected to the dedicated White House internet network (Autonomous System AS2650) were actively running residential proxy software. This software effectively rendered the network’s high-privilege Internet Protocol (IP) addresses available for rent to anonymous third parties worldwide.
The discovery highlights a pervasive and insidious blind spot in modern digital defense: the invisible integration of monetized proxy software into seemingly harmless desktop applications and mobile tools. By installing these apps on devices that connect to secure government networks, employees have unwittingly opened a backdoor into one of the most heavily guarded digital estates on the planet.
According to threat intelligence firm Layer3 Intel, persistent proxy activity was tracked across the White House’s AS2650 network over a crucial four-week window between October 5 and November 3. During this period, security investigators documented 236 separate instances where proxy traffic successfully exited through the White House infrastructure.
Worse still, the investigation revealed that this was not an isolated incident involving a single rogue service. Layer3 Intel identified 28 distinct residential proxy services capable of routing traffic through the White House network. Among them was Infatica, a controversial proxy provider founded by Vladimir Fomenko—a Russian national whose previous web hosting venture, King Servers, served as the operational launchpad for the 2016 cyberattacks against state election databases in Arizona and Illinois.
The implications of this exposure extend far beyond standard data leakage. For a cost as low as 60 cents per gigabyte, cybercriminals, state-sponsored espionage groups, or malicious botnets can bypass traditional perimeter security controls. By leveraging these proxy networks, bad actors can masquerade as official White House IP addresses to execute fraud, evade detection, and probe internal enterprise networks.
Detailed Chronology: How the White House Network Was Compromised
The timeline of the discovery underscores the casual, almost accidental nature by which modern threat intelligence exposes major vulnerabilities.
October 5 to November 3: The Observation Window
During routine global mapping of residential proxy exit nodes, researchers at Layer3 Intel noticed anomalies originating from AS2650—an autonomous system reserved exclusively for the Executive Office of the President.
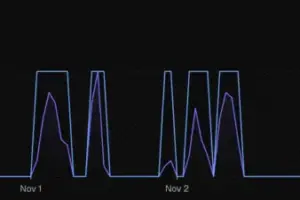
Rather than deploying targeted probes against the White House, researchers stumbled upon the activity simply by requesting global rotating access through public proxy networks. Over the course of 30 days, Layer3 detected proxy exit nodes operating out of the White House network on 26 separate days, utilizing six distinct IP addresses.
Behavioral analysis of the traffic revealed a distinct temporal pattern: the vast majority of the unauthorized proxy activity occurred during evening hours, specifically between 5:00 PM and midnight. This cadence strongly suggests that the compromised devices belonged to staffers working late hours, accessing personal accounts, or using government-linked hardware for personal tasks outside core business hours.
Integration with Infatica and Windows 11
As the investigation deepened, threat intelligence platform Synthient published telemetry via X (formerly Twitter) linking a significant portion of the AS2650 proxy traffic to Infatica. The activity was traced to multiple Windows 11 installations running Infatica’s background software.
Infatica operates by embedding its proprietary software development kits (SDKs) into "free" consumer-facing mobile and desktop applications. Users download these apps—often utilities, games, or browser extensions—unaware that the fine print authorizes the application to utilize their device’s internet connection as a traffic relay.
The connection to Infatica brought immediate historical gravity to the situation. Infatica’s founder, Vladimir Fomenko, is well-known to Western intelligence and cybersecurity agencies. In 2016, Fomenko’s hosting company, King Servers, provided the infrastructure for six of the eight IP addresses utilized by Russian state-sponsored actors to breach and exfiltrate voter registration databases in Illinois and Arizona. While there is no direct evidence that the current White House proxy nodes are being actively weaponized by Russian intelligence agencies, the architectural link to an infrastructure builder with historical ties to state-sponsored election hacking introduces acute national security concerns.
The Scale of the Multi-Vendor Breach
Layer3 Intel’s comprehensive audit of the AS2650 network yielded an even more shocking revelation: Infatica was merely one of 28 separate residential proxy providers that had successfully established exit nodes within the White House infrastructure.
"This is public access," the Layer3 Intel research team noted in an official post-mortem. "Anybody can obtain it by signing up to a public residential proxy service, paying a few dollars and sending requests through it. We did not selectively target this network or try to make our probes exit from it. We caught this by chance…"
Supporting Context & Metrics: The Global Threat of Residential Proxies
To understand the severity of the White House incident, one must examine the sprawling, largely unregulated multi-million-dollar residential proxy ecosystem.
What Are Residential Proxies?
Unlike traditional data center proxies (which use servers hosted by cloud providers and are easily flagged and blocked by website firewalls), residential proxies route internet traffic through real, residential IP addresses assigned by Internet Service Providers (ISPs) to everyday consumers.
When a user’s device is co-opted into a proxy network, anyone willing to pay a small subscription fee can rent that user’s IP address. To a target website, any malicious activity—such as credential stuffing, automated account takeovers, advertising fraud, or massive data scraping for artificial intelligence models—appears to originate from the innocent residential user’s home or office network.
The Local Network Threat (The Kimwolf Connection)
Residential proxies do not merely expose outgoing traffic; they present a catastrophic lateral movement risk to local networks.
In late 2025 and early 2026, security researchers uncovered widespread exploitation of vulnerabilities embedded directly within residential proxy architectures. Threat actors realized they could leverage compromised proxy endpoints to scan the local networks (LANs) to which those endpoints were attached.
In January 2026, Synthient Founder Ben Brundage exposed the Kimwolf botnet, which actively stalked local networks via proxy software, probing connected devices for vulnerabilities to infect with malware.
"Some of these resellers sell bandwidth for as low as 60 cents a Gigabyte, that means for less than a dollar you can gain access into some of the most confidential and trusted networks," Brundage explained in an interview with KrebsOnSecurity. "The reseller ecosystem further enables this with any criminal able to buy access while skipping KYC [Know Your Customer] processes."
If a staffer brings an infected laptop or a mobile device running a proxy-enabled app into the White House and connects it to the internal Wi-Fi or Ethernet, that device can theoretically act as a bridgehead. Cybercriminals can use the proxy node not just to hide their web traffic, but to scan internal, air-gapped, or restricted administrative subnets for exploitable vulnerabilities.
A Corporate and Government Epidemic
The White House is far from alone in facing this silent contagion. Because proxy SDKs are hidden inside popular productivity tools, browser extensions, and mobile utilities, corporate and government employees routinely bring these hazards into secure workplaces.
Industry data reveals the breathtaking scale of this infiltration:
- Government Networks: In a January 2026 webinar, proxy tracking service Spur identified active residential proxies operating within nearly 300 government-owned and operated networks.
- Critical Infrastructure: Spur’s telemetry also uncovered proxies across 318 utility companies, 166 healthcare organizations and hospitals, and 141 financial and banking institutions.
- Corporate Vulnerability: Security firm Infoblox published findings showing that 65% of its entire enterprise customer base had internal devices querying residential proxy-related domains.
Official Statements and Institutional Response
As of the publication of this report, the White House has not formally responded to requests for comment regarding the Layer3 Intel and Synthient disclosures.
The absence of an immediate public statement underscores the delicate nature of the discovery. Federal agencies and Executive Office IT administrators must now balance public transparency with the urgent requirement to audit, identify, and sanitize every device connected to AS2650.
Cybersecurity analysts point out that mitigating this threat requires moving beyond traditional perimeter defenses. Because residential proxy traffic originates from legitimate-looking applications and standard consumer devices, legacy firewalls and intrusion detection systems (IDS) frequently fail to flag the outbound beacons as malicious.
Instead, organizations must implement strict Mobile Device Management (MDM) solutions, enforce rigorous application whitelisting, and deploy continuous network behavioral monitoring designed to spot outbound beaconing to known proxy broker domains and ASNs.
Future Outlook: Securing the Digital Perimeter in the Age of Monetized SDKs
The revelation that public proxy services have successfully turned the White House into a commercial exit node serves as a watershed moment for modern enterprise security. It shatters the illusion that physical proximity or secure campus environments are sufficient to protect high-value institutional networks.
The Need for Stringent Software Supply Chain Audits
The root cause of the White House proxy leak lies in the shadow economy of software monetization. App developers, seeking alternative revenue streams, frequently accept financial incentives from proxy brokers to bundle tracking and proxy SDKs into free utilities.
For government and corporate entities, the path forward demands a zero-tolerance policy toward unverified software on any device capable of accessing sensitive networks. Security teams must implement aggressive Endpoint Detection and Response (EDR) tooling capable of identifying unauthorized background network tunneling, proxy daemons, and unexpected external socket connections.
Regulatory and Marketplace Reform
Pressure is mounting on regulatory bodies to hold proxy brokers accountable for failing to implement basic Know Your Customer (KYC) standards. When services can sell encrypted bandwidth for pennies without verifying who is purchasing access, they functionally act as arms dealers for the cybercrime underground. Without mandatory compliance frameworks, robust abuse-reporting mechanisms, and legal penalties for proxy brokers operating unchecked infrastructure, high-value networks will remain exposed.
Ultimately, the White House proxy incident demonstrates that the traditional boundaries separating personal digital habits from enterprise security have vanished. In an interconnected world where a dollar’s worth of rented bandwidth can pierce the defenses of the Executive Office of the President, vigilance must extend all the way down to the individual application code running on every employee’s pocket device.