Executive Overview
In a dramatic convergence of international law enforcement and the high-stakes underworld of cyber extortion, federal agents have arrested a high-profile Canadian cybersecurity executive in Pennsylvania. The arrest is directly tied to an expansive, high-priority federal investigation into the notorious ShinyHunters hacking group—a cybercrime collective that recently breached the Federal Bureau of Investigation (FBI) itself, absconding with sensitive data belonging to thousands of federal agents.
The suspect, identified in federal court records as Edward Dubrovsky (with the last name occasionally misspelled as Dobrovsky in initial dockets), is a prominent figure in the incident response community. Dubrovsky is a managing director-level security professional, author of the 252-page textbook Cyber Extortion Strategic Response, and a key figure associated with several Canadian cybersecurity firms specializing in ransomware advisory and negotiation. His apprehension occurred during a visit to Philadelphia for a major cyber insurance conference where his firm was a premier sponsor.
This high-profile arrest highlights a murky and legally perilous intersection within the cybersecurity industry: the fuzzy boundary between authorized ransomware negotiation, incident response consulting, and criminal conspiracy. As federal prosecutors in the Eastern District of Texas take charge of the sprawling prosecution, investigators are examining whether specialized advisory firms crossed ethical and legal lines when dealing with threat actors.
The developments arrive on the heels of a tumultuous period for federal law enforcement. ShinyHunters recently humiliated the Bureau by infiltrating its online recruitment portal, pillaging deep personal records—including medical and psychiatric histories and tactical unit assignments—and taunting investigators online. With international police operations closing in on key nodes of the syndicate, the global dragnet is tightening, and sources indicate that further charges against executives in the ransomware negotiation ecosystem may be imminent.
Detailed Chronology of Events
The sequence of events leading to Dubrovsky’s arrest reads like a geopolitical thriller, moving rapidly from international cyber conferences to federal holding facilities.
The Cyber Risk Summit in Philadelphia (October 5–7, 2026)
Edward Dubrovsky traveled to the United States to attend the annual Cyber Risk Summit held at the Loews Philadelphia Hotel. According to conference schedules and public listings, the event attracted leading figures in cyber insurance, risk management, and incident response. Dubrovsky, slated to participate in high-level discussions surrounding global ransomware advisory, negotiation, and settlement strategies, was publicly associated with CyberSteward, a Canadian security firm and primary sponsor of the event. (Public filings and LinkedIn histories also tie him to Cypfer, another Canadian security firm where he previously served before a management departure in late 2025).
The Arrest and Initial Legal Filings (October 8, 2026)
On October 8, federal law enforcement operations culminated in the apprehension of Dubrovsky in Pennsylvania. Court records reflect that he was charged with serious federal offenses, including conspiracy to threaten to impair the confidentiality of information with the intent to extort money and interference with commerce by threats.
While the core complaint and key evidentiary documents were swiftly placed under seal by the court, a docket summary was indexed via public legal repositories like CourtListener. The records noted that a 54-year-old Edward Dubrovsky was initially booked into a federal detention facility in Philadelphia operated by the U.S. Bureau of Prisons.
Transfer to the Epicenter of the Investigation (October 9, 2026)
Recognizing the broader jurisdictional ties to the nationwide ShinyHunters probe, a notice was filed on October 9 transferring Dubrovsky’s case to the Eastern District of Texas. Multiple investigative sources confirm that the U.S. Attorney’s Office and the FBI field office in Texas have become the central command hub for the overarching ShinyHunters conspiracy case. As of initial court appearances, Dubrovsky remained unrepresented by retained counsel, with public defender appointments pending.

Supporting Context & Metrics: The Anatomy of the ShinyHunters Threat
To understand the gravity of the charges against Dubrovsky, one must examine the operational blueprint and recent escalation of the ShinyHunters syndicate.
Methods of Operation
ShinyHunters has historically operated as a ruthless data-siphoning and extortion syndicate. The group typically gains initial access to corporate environments through sophisticated phishing campaigns, credential harvesting, and attacks against software-as-a-service (SaaS) providers. Once inside, they exfiltrate massive tranches of proprietary corporate records, customer databases, and intellectual property. Rather than deploying traditional ransomware cryptolockers to halt operations, the group relies on pure extortion: threatening to leak stolen data publicly on dark web forums or auction sites unless exorbitant ransom demands are satisfied.
Financial Impact
According to intelligence released by federal law enforcement, ShinyHunters has proved devastatingly lucrative. Over the course of the year, the syndicate has successfully extorted more than $70 million from corporate and institutional victims globally.
The FBI Breach and the Rise of "Rey"
The conflict between ShinyHunters and American law enforcement reached a boiling point following a series of aggressive international operations. Last month, Dutch police executed raids resulting in the arrest of Pepijn van der Stap, a reformed hacker tied to the syndicate. Seized electronic devices from Van der Stap provided FBI cyber investigators with a wealth of digital forensic evidence.
In the wake of Van der Stap’s arrest, leadership within the hacker collective shifted to an operative known online as "Rey." Assuming operational control, Rey began aggressively taunting the FBI, weaponizing a massive data breach against the Bureau itself. The compromised data originated from the FBI’s online recruitment portal, exposing sensitive files detailing:
- Individual agent names and personal identifiers
- Specific tactical unit assignments and professional specializations
- Highly confidential medical and psychiatric records
The Net Tightens: Detentions and Corporate Extortion
Law enforcement pressure quickly forced Rey’s hand. Following international investigative coordination, Reuters reported that "Rey"—identified as a teenager named Saif Al-din Khader—had been detained and was actively cooperating with FBI investigators.
Prior to his apprehension, Khader and his cell had targeted high-value industrial sectors. Public disclosures revealed that ShinyHunters attempted to extort a major navigation and digital aviation unit that had been divested by aerospace giant Boeing in late 2025.
Official Statements and Industry Fallout
The involvement of an executive from a prominent incident response and negotiation firm has sent shockwaves through the cybersecurity industry. The intersection of extortion advisory services and criminal syndicates has long been a whispered gray zone among risk executives, but public federal indictments mark a watershed moment.
FBI Silence and Executive Posturing
Thus far, FBI Director Kash Patel and the Bureau’s press office have maintained a tightlipped posture regarding the specifics of Dubrovsky’s indictment, issuing sparse social media updates acknowledging ongoing operations while declining interview requests regarding the sealed indictments.

Corporate Distancing
As details of Dubrovsky’s professional background emerged, corporate entities rushed to clarify their organizational boundaries. A spokesperson for Cypfer issued a clarifying statement noting that Dubrovsky was never a founder or co-founder of the firm, contrary to claims on his professional social media profiles, but rather served strictly as a managing director before his resignation in November 2025.
Similarly, associates at CyberSteward—the firm Dubrovsky was representing at the Philadelphia conference—have largely declined immediate comment as legal counsel scrambles to address the fallout.
The Paradox of the Ransomware Expert
The irony of Dubrovsky’s arrest is compounded by his literary contributions to the field. In his 252-page book, Cyber Extortion Strategic Response, Dubrovsky explicitly warned organizations about the dangers of mishandling threat actors. A prominent excerpt from the book’s promotional material reads:
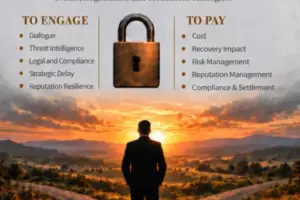
"At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
Federal prosecutors will now test whether Dubrovsky’s own advisory engagements stayed safely within the bounds of defensive negotiation, or crossed the line into active participation, material support, or conspiracy with the ShinyHunters enterprise.
Future Outlook
The arrest of Edward Dubrovsky is unlikely to remain an isolated incident. Industry insiders and legal experts suggest that the federal investigation—now heavily consolidated under the supervision of the Texas FBI field office—is entering a highly aggressive phase.
As digital forensic examiners comb through the digital assets seized from Pepijn van der Stap, Saif Al-din Khader ("Rey"), and now Dubrovsky, investigators are reportedly scrutinizing the broader ecosystem of third-party negotiators. Sources close to the investigation indicate that additional charges against principals and intermediaries at other cyber extortion advisory firms may be forthcoming in the coming weeks.
For the cybersecurity and cyber insurance industries, this case serves as a stark warning. As governments worldwide crack down on ransomware syndicates and the financial channels that sustain them, the legal tolerances for dealing with cybercriminals are narrowing sharply. The days of operating in an unregulated gray zone of shadow negotiations are drawing to a close, and accountability is stretching far beyond the core hackers sitting behind keyboards to encompass those who facilitate dialogue in the shadows.
This is a developing story. Updates, court filings, and official statements will be added as new information becomes available.