The shadowy infrastructure of the prolific data extortion syndicate known as ShinyHunters has suffered a catastrophic blow. According to international investigative reports and cybersecurity intelligence, a teenager operating out of Amman, Jordan, under the hacker handle "Rey"—identified as Saif Al-din Khader—has been detained by local authorities and is reportedly cooperating extensively with the Federal Bureau of Investigation (FBI).
Khader’s apprehension occurred precisely as the collective he allegedly fronted was deep into an aggressive extortion campaign targeting Jeppesen ForeFlight, a digital aviation and navigation unit recently divested by global aerospace titan Boeing. This high-stakes operation inadvertently drew a dangerous circle around the suspect’s personal life: Khader’s father is heavily tied to Royal Jordanian Airlines, a national carrier operating a long-haul fleet built primarily by Boeing.
Simultaneously, the broader ShinyHunters enterprise has devolved into a chaotic decentralized franchise. The group’s recent stunts—ranging from zero-day mass exploitation of Oracle PeopleSoft servers to a brazen, retaliatory hack of the FBI’s own recruitment database—have laid bare a shifting underground economy. This syndicate operates less like a traditional hacker crew and more like the "Dread Pirate Roberts" persona from The Princess Bride: a transferable digital banner adopted by successive waves of opportunistic freelancers. With core members imprisoned in France, a Dutch "reformed" hacker arrested in Amsterdam over alleged murder-for-hire plots, and online trackers aggressively doxing the teenage ringleader, the saga of modern cyber extortion has reached a volatile and unpredictable inflection point.
Detailed Chronology: Zero-Days, Raids, and the Capture of ‘Rey’
The unraveling of the modern ShinyHunters apparatus accelerated through the summer and autumn of 2026, marked by high-profile zero-day exploits, international police coordination, and a digital turf war on encrypted messaging apps.
The PeopleSoft Campaign and the FBI Breach
In June 2026, threat actors associated with the ShinyHunters brand began mass-exploiting a critical zero-day vulnerability (CVE-2026-35273) affecting Oracle PeopleSoft, a widely deployed software-as-a-service (SaaS) platform used across industries for human resources, benefits administration, and payroll. Initial intelligence gathered by security firms indicated that the group’s primary, albeit initially unsuccessful, target was the FBI’s internal PeopleSoft database.
Although Oracle rapidly deployed a patch and firms like Mandiant issued web application firewall (WAF) mitigation rules, the hackers adapted. By utilizing sophisticated URL-encoding tricks to bypass WAF defenses, ShinyHunters successfully breached dozens of corporate, government, and educational networks.
By mid-May, the fallout intensified when the FBI published a stinging flash notice warning organizations against paying ransoms to the collective. Stung by the agency’s public advisory—which characterized the group’s tactics as erratic and warned of psychological harassment campaigns—ShinyHunters retaliated. The hackers leveraged their PeopleSoft exploits to breach an Accenture contractor portal linked to the FBI’s recruitment pipeline. This breach exposed the sensitive personal and professional data of over 5,000 FBI personnel, including unit specializations, medical records, and psychiatric profiles.
The Arrest of ‘Umbreon’ and Rey’s Desperate Gamble
The investigation took a dramatic turn in mid-September. On the evening of September 15, Dutch police executed a high-profile tactical raid in Amsterdam—reportedly utilizing flash-bang grenades—to arrest 24-year-old Pepijn van der Stap. Van der Stap, a convicted cybercriminal previously operating under the handle "Umbreon," had recently cultivated a public persona as a reformed security professional working as an "offensive security lead" at a Dutch firm called Neo Security. Authorities, however, suspected him of continuing his data theft and extortion activities under the ShinyHunters umbrella.
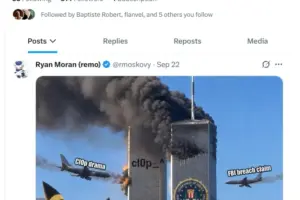
As news of Van der Stap’s arrest broke, "Rey" (Saif Al-din Khader) seized the opportunity to consolidate power. Assuming control over the dormant ShinyHunters brand, Rey launched a public relations blitz on Twitter/X and Telegram. He boasted about stealing sensitive FBI data and extorting the infamous Cl0p ransomware cartel. In an elaborate attempt to misdirect investigators, Rey posted taunting memes featuring the Pokémon character Umbreon—direct references to Van der Stap’s former alias—to frame the Dutchman for the attacks.
The Net Tightens in Amman
Rey’s bravado was short-lived. Cybersecurity researchers, including Brian Krebs, had previously unmasked Rey in late 2025 as a teenage hub for various ransomware affiliates. By late September 2026, investigative pressure reached a boiling point.
On October 3, Reuters broke the news that Jordanian authorities had detained Khader in Amman following a coordinated intelligence-sharing operation with the FBI. Rather than standing trial as an unyielding cyberlord, Khader reportedly began cooperating with federal agents, providing actionable intelligence on fellow hackers and syndicate members. Within hours of inquiries being sent to his family, Rey scrubbed his social media footprint, though his GitHub cybersecurity blog—which featured a detailed doxing post exposing two Russian developers behind the Cl0p ransomware—remained online.
Supporting Context & Metrics: The Anatomy of a Cybercrime Franchise
To understand how a teenager from Jordan managed to paralyze high-profile enterprise targets, one must examine the evolution of ShinyHunters from a centralized elite crew into a decentralized criminal franchise.
The Franchise Model
The Founders: The original ShinyHunters burst onto the scene around 2019, responsible for historical data breaches spanning billions of stolen records. Most of those core members—predominantly French nationals—were eventually rounded up and imprisoned by European law enforcement.
The Successors: Into the vacuum stepped independent freelancers, affiliates, and juvenile actors like Rey. Rather than maintaining a rigid corporate hierarchy, these individuals bought or inherited old PGP keys, forum accounts, and brand names (such as BreachForums aliases) to "larp" as the original syndicate.
The Business Arrangement: Investigations reveal that newer iterations of ShinyHunters operated on a commission model. Freelancers fed stolen software-as-a-service (SaaS) credentials to the group, which then negotiated extortion demands, paying out a 25% to 30% cut to the initial access brokers.
Quantifying the Damage
$200 Million+: Estimated cumulative enterprise damages tied to the decentralized network of affiliates operating under the ShinyHunters banner over preceding months.
5,000+ Personnel: FBI recruitment records compromised via the Accenture-managed PeopleSoft vulnerability.
€1.5M to €2.7M: Prosecutorial estimates of funds netted by legacy actors like Van der Stap during his primary active years prior to his initial 2023 conviction.
$10.55 Billion: The valuation of Boeing’s November 2025 divestiture of Jeppesen ForeFlight to private equity firm Thoma Bravo—the very subsidiary whose extortion cycle triggered the urgent international manhunt for Rey.
Official Statements and Corporate Fallout
The convergence of corporate spin-offs, national security breaches, and localized arrests has drawn carefully managed statements from the corporate and law enforcement entities involved.
Boeing and Jeppesen ForeFlight
The targeting of Jeppesen ForeFlight introduced immediate operational and physical security concerns, given the company’s critical role in digital aviation navigation.
"We are aware of claims by a threat actor regarding data allegedly associated with Boeing and our former subsidiary Jeppesen ForeFlight," a Boeing spokesperson stated. "Estamos actively reviewing the matter with the Jeppesen ForeFlight team."
Jeppesen ForeFlight minimized the disruption in a subsequent public statement:
"Based on our investigation to date into this claim and proactive security posture, there was no impact to our operations or products."
Neo Security and the Amsterdam Raid
The situation surrounding Pepijn van der Stap took an even darker turn when Dutch media outlet RTL reported that investigators suspected the former "reformed" hacker of attempting to orchestrate at least two contract murders abroad. Benjamin Korper, owner of Neo Security, admitted that Dutch forensic units raided his offices on September 15, though internal audits found no evidence that Van der Stap had compromised Neo’s own client systems.
The FBI and Industry Security Advisories
The FBI’s May 2026 flash notice underscored the psychological warfare tactics favored by the post-2025 ShinyHunters cells:
"[Threat actors] may use aggressive harassment strategies, including sending threatening text messages and phone calls to victims and their family members, swatting victims, or falsely claiming to possess sensitive or compromising photographs or videos that frequently do not exist."
In defense of their actions, representatives for the hackers told The Register that their decision to target the FBI was purely a public relations maneuver designed to counteract what they viewed as misleading agency advisories that were harming their extortion business model.
Future Outlook: The End of the Brand?
The simultaneous detention of Saif Al-din Khader in Amman and the dramatic arrest of Pepijn van der Stap in Amsterdam mark the effective twilight of the modern ShinyHunters incarnation.
For the cybercriminal underground, the ordeal serves as a cautionary tale about the perils of brand association. As highlighted by rival Telegram channels like "The Battle," which relentlessly doxed and mocked Rey for weeks, the teenager fundamentally misunderstood the ecosystem he sought to command. By co-opting a burned, highly monitored brand name while lacking the operational security of his predecessors, Rey invited intense regulatory scrutiny that ultimately destroyed his network.
Moving forward, federal law enforcement agencies are shifting their focus to the remaining digital freelancers who supply corporate credentials to ransomware brokers. However, as long as the underground economy rewards initial access brokers with lucrative cryptocurrency payouts, the hydra-like nature of cybercrime guarantees that new brands will rise from the ashes of ShinyHunters—even if the teenagers attempting to wear the crown find themselves trading their keyboards for prison cells or cooperation agreements.