Executive Overview
The United Kingdom’s recent enforcement action against the cryptocurrency platform Cryptomus marks a pivotal escalation in the global fight against illicit digital finance, sanctions evasion, and transnational cybercrime. On October 8, the U.K. government officially slapped comprehensive economic sanctions on Cryptomus—a notoriously nimble payment processor that security experts have long tied to ransomware campaigns, narcotics trafficking, darknet market operations, and financial fraud.
Operating under a rotating cast of corporate names and front entities, including Certa Payments and Xeltox Enterprises, Cryptomus has functioned for years as a vital financial conduit. Its infrastructure has systematically helped the Russian government and associated financial institutions bypass stringent Western economic restrictions. In addition to targeting Cryptomus, the U.K. Foreign, Commonwealth & Development Office levied similar restrictive measures against parallel virtual payment platforms VexPay, TokenSpot, and the Tsunami Payments service.
While Canada previously attempted to curb the platform’s illicit activities with a historic CAD $176 million fine in late 2025, that penalty ultimately proved uncollectible and ineffective at halting operations. The U.K.’s new sanctions represent a far more lethal blow: freezing all domestic assets held at British financial institutions, prohibiting U.K. companies from engaging in any commercial or virtual business with the platform, and striking at the core of the infrastructure supporting Russia’s wartime economy.
Crucially, this regulatory maneuver carries profound geopolitical significance. Blockchain investigators and cybersecurity analysts note that this is the first known instance of a "Five Eyes" intelligence-sharing nation (comprising Australia, Canada, New Zealand, the United Kingdom, and the United States) officially sanctioning a cryptocurrency operation incorporated within the jurisdiction of another Five Eyes member. This action exposes deep vulnerabilities in corporate registration loopholes, shadow regulatory bodies, and the cross-border movement of illicit digital assets.
Detailed Chronology: From Certa Payments to Heleket
The evolution of Cryptomus is a masterclass in corporate camouflage. To understand how the platform managed to evade international oversight for years, one must trace its deliberate trajectory of rebranding, restructuring, and evasion.
Emergence and Early Expansion (2022–2024)
Emerging onto the digital asset landscape in 2022, Cryptomus initially positioned itself as a standard, high-volume payment gateway for e-commerce. However, behind its polished interface lay an infrastructure purposefully designed to welcome high-risk clientele. Operating concurrently under corporate identities such as Certa Payments and Xeltox Enterprises, the platform established a supposed corporate headquarters at a shared Vancouver office address. Investigators quickly discovered that this location served as a ghost address for dozens of unrelated foreign currency dealers and money transfer businesses, housing none of them physically.
By late 2024, investigative reports—including landmark deep-dives by cybersecurity journalist Brian Krebs—unmasked Cryptomus as a primary financial engine for dozens of underground Russian cryptocurrency exchanges and websites specializing in cybercrime-as-a-service. The platform made its mark by converting illicitly obtained cryptocurrency into clean cash accessible through Russian banking channels, directly subverting Western sanctions.
The Canadian Fine and the Birth of "Heleket" (2025)
As the scale of illicit transactions processed by Cryptomus became impossible to ignore, regulatory pressure intensified. In October 2025, Canadian authorities levied a record-shattering CAD $176 million fine against Cryptomus for severe violations of anti-money laundering (AML) regulations.
Rather than complying with regulatory mandates or instituting robust identity verification protocols, Cryptomus executed a classic shell game. The platform formally appealed the Canadian penalty while simultaneously spinning up a parallel, unhindered service under the brand name “Heleket.”
Heleket was designed to operate precisely where Cryptomus left off: offering frictionless, zero-KYC (Know Your Customer) payment processing to the exact network of cybercriminals, fraudsters, and sanctions-evading entities that had relied on its predecessor. Telegram support channels for Heleket brazenly denied any corporate affiliation with Cryptomus, even as blockchain tracing tools mapped identical wallet infrastructures, administrative backends, and customer service personnel managing both operations.
The U.K. Intervention (October 2026)
The turning point arrived on October 8, 2026, when the U.K. government severed the platform’s financial lifeline. Recognizing that administrative fines are routinely ignored by decentralized or deliberately obfuscated crypto enterprises, London issued sweeping economic sanctions.

Within hours of the sanctions announcement, the operational stability of the platform fractured. Telegram bots and customer service portals for both Cryptomus and Heleket flooded with automated and manual messages stating that the platforms were suddenly experiencing technical difficulties and were unable to process transactions. For the first time in its operational history, the chameleonic network faced an existential threat that asset
freezes and business bans could deliver.
Supporting Context & Metrics: The Scale of Illicit Finance
The sheer magnitude of capital flowing through Cryptomus and its spin-off entities underscores why international intelligence and blockchain analysis firms elevated the platform to a top-tier national security threat.
Transaction Volumes and Illicit Counterparties
According to comprehensive data compiled by blockchain analytics titan TRM Labs in April 2026, Cryptomus had processed an astonishing $7 billion in transactions since its inception in 2022. This staggering volume was not generated by legitimate retail merchants; rather, it was heavily saturated with funds linked to:
- Global ransomware syndicates demanding extortion payouts.
- Vendors distributing child sexual abuse material (CSAM).
- State-aligned and independent terrorist financing networks.
- International human trafficking operations.
- Darknet marketplaces trading in narcotics, stolen credentials, and zero-day exploits.
Furthermore, a critical post-mortem published by Chainalysis on October 8, 2026, highlighted the unprecedented scale of illicit fund ingestion managed by the network. Chainalysis noted that Cryptomus and Heleket received more illicit funds across tracked categories than traditional cryptocurrency "mixers" (tools designed to obfuscate transaction trails) in their datasets.
Most alarmingly, the number of distinct illicit counterparties transacting with the platform surged to more than 900 unique entities in a single month in late 2025. This metric demonstrates that Cryptomus was not merely a passive conduit, but an active, preferred liquidity hub for the global underground economy.
The KYC Paradox
Data from blockchain intelligence firms revealed a telling trend regarding Cryptomus’s transaction volumes. When the platform occasionally yielded to international pressure by experimenting with superficial Know Your Customer (KYC) rules, its transaction volume plummeted dramatically. Recognizing that strict verification requirements alienated its core customer base of cybercriminals and sanctions-evaders, the platform quickly pivoted back to frictionless, anonymous transaction processing—ultimately birthing the Heleket ecosystem to bypass regulatory friction entirely.
Official Statements and Industry Analysis
The international response to the U.K. sanctions has been overwhelmingly positive within the cybersecurity and blockchain intelligence communities, highlighting a growing consensus that traditional regulatory fines are insufficient against transnational crypto crime syndicates.
Chainalysis: Targeting Wartime Infrastructure
In its official October 8 assessment, Chainalysis emphasized that the U.K.’s actions extend far beyond penalizing a single bad actor; they represent a direct strike against the financial architecture sustaining Russia’s wartime economy:
"Cryptomus and Heleket have emerged as major payment hubs for illicit activity," Chainalysis wrote. "Together, these services received more illicit funds across tracked categories than the mixers in our dataset, and the number of illicit counterparties surged to more than 900 in a single month in late 2025."
Richard Sanders on the Limits of Fines vs. Sanctions
Prominent blockchain analyst and investigator Richard Sanders, who spent months painstakingly mapping Cryptomus’s complex infrastructure and test-transacting with its network of clients, provided crucial context on why the U.K. sanctions are uniquely effective. Comparing the outcomes of Canadian fines versus British sanctions, Sanders emphasized the legal and operational distinction:

"A fine doesn’t stop a cryptocurrency payment processor from processing payments," Sanders wrote in a widely shared professional analysis. "Sanctions kill the operation. The distinction matters."
Sanders also highlighted the unprecedented nature of a Five Eyes member nation sanctioning an entity incorporated within another Five Eyes territory. This jurisdictional overlap exposed critical friction points in how Western nations share intelligence, regulate corporate formations, and address cross-border financial crime perpetrated by allies against mutual adversaries.
Anatomy of a Phantom Regulator: The Western Sahara Connection
One of the most bizarre and illuminating revelations unearthed during investigations into Cryptomus involves the origin of its operational authority. How do shadowy cryptocurrency platforms operating out of Vancouver and serving Russian cybercrime syndicates acquire the legal facade necessary to present themselves as legitimate international financial institutions?
The answer leads to a complex web of shell companies, proxy owners, and phony regulatory bodies positioned in disputed geopolitical territories.
The 25-Year-Old Ukrainian Director and the Phantom Regulator
Investigative deep-dives into the corporate registry documents of Certa Payments (Cryptomus’s parent company) revealed that its sole shareholder was a 25-year-old Ukrainian woman. Beyond her role at Certa Payments, she simultaneously headed several other corporate entities, most notably the WS Management and Advisory Corporation.
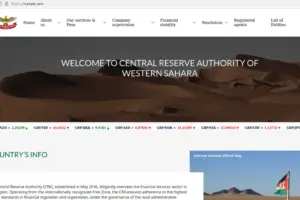
This corporation billed itself as an exclusive, authoritative regulatory body responsible for licensing cryptocurrency enterprises, foreign exchange (forex) brokers, and online gaming companies incorporated within the Western Sahara—a disputed region in northwest Africa not widely recognized as a sovereign nation.
The Fake Regulatory Bureaucracy
The purported regulatory body operated through a web-based portal located at crasadr.com, representing the fictional Central Reserve Authority of the Western Sahara (CRASADR). The website aggressively marketed its services to shady online enterprises, promising assistance with offshore bank account setup, corporate formation, and the acquisition of prestigious gaming and forex licenses.
Forensic web infrastructure analysis conducted by investigators revealed undeniable overlaps between Cryptomus’s operational footprint and this phantom regulator. For instance, one of Certa Payments’ historical domains (certa.website) shared a web server with 12 other distinct domains, including rasd-state.ws—the digital home of the Central Reserve Authority of the Western Sahara.
By weaponizing jurisdictional gray zones, fake regulatory bodies, and indifferent corporate registration systems in Western nations, Cryptomus manufactured a veneer of institutional legitimacy. This elaborate facade allowed them to interface with traditional banking partners and obscure the true nature of their operations from compliance officers worldwide.
Future Outlook
The U.K.’s decisive enforcement action against Cryptomus, Heleket, VexPay, TokenSpot, and Tsunami Payments establishes a critical precedent for the future of international cybercrime enforcement.
- The Shift Toward Asset Freezes: The limitations of monetary penalties—as demonstrated by Canada’s uncollectible CAD $176 million fine—have become abundantly clear. Future regulatory strategies are expected to rely more heavily on immediate asset freezes, criminal indictments, and coordinated international sanctions that disrupt the underlying technical and banking infrastructure of illicit processors.
- Scrutiny on Corporate Shells: The exposure of the Western Sahara phantom regulator (
crasadr.com) highlights a glaring loophole in global corporate registries. Governments within the Five Eyes alliance and the Financial Action Task Force (FATF) are likely to face mounting pressure to tighten verification standards for foreign corporate filings, shell company formations, and offshore licensing bodies. - The Whack-a-Mole Phenomenon: While sanctions effectively cripple specific platforms like Cryptomus and Heleket, blockchain intelligence firms warn that the underlying demand for sanctions-evasion and cybercrime payment processing remains high. Illicit networks will undoubtedly attempt to rebrand, fragment, or migrate to decentralized protocols. However, the aggressive cross-border posture demonstrated by the U.K. signals that law enforcement agencies are increasingly equipped to track, unmask, and dismantle these chameleonic operations wherever they attempt to hide.