WASHINGTON — In a startling cybersecurity oversight, security researchers have uncovered evidence that multiple devices connected to the dedicated internet network of the Executive Office of the President have been acting as commercial residential proxy nodes. This misconfiguration has effectively rented out portions of the White House’s secure internet infrastructure to anonymous external buyers, including entities tied to foreign intelligence-linked operations.
The alarming discovery highlights a pervasive, multi-billion-dollar shadow ecosystem of proxy services that turns everyday consumer hardware—and, apparently, high-security government networks—into open-door relay stations for web traffic. According to telemetry gathered by cybersecurity firms, the activity persisted across multiple weeks, exposing sensitive governmental IP space to potential espionage, malicious reconnaissance, and untracked cyberattacks.
Executive Overview
The unfolding incident centers around the unauthorized operation of residential proxy software on computers and mobile devices linked to AS2650, the distinct Autonomous System number reserved exclusively for the Executive Office of the President.
Between October 5 and November 3, threat intelligence firm Layer3 Intel detected persistent proxy beaconing originating from this elite government network. Independent tracking by proxy-monitoring firm Synthient confirmed that the activity was directly associated with Infatica, a commercial proxy provider founded by Vladimir Fomenko, a Russian national whose past hosting infrastructure was famously implicated in state-sponsored cyberattacks against U.S. election databases in 2016.
Compounding the severity of the discovery, Layer3 Intel reported that Infatica was not an isolated outlier. A comprehensive audit of AS2650 revealed that 28 separate residential proxy networks were capable of routing traffic outward through White House IP addresses during the observation window. For a cost of mere pennies per gigabyte, any individual on the internet could seamlessly lease a slice of White House internet connectivity to obscure their digital footprint.
Detailed Chronology & Technical Findings
Discovery and Detection
The breach was not uncovered through classified government introspection, but rather by chance. Analysts at Layer3 Intel were probing global rotating proxy pools as part of routine threat-hunting operations when they noticed an anomalous frequency of exit nodes matching government-allocated IP blocks.
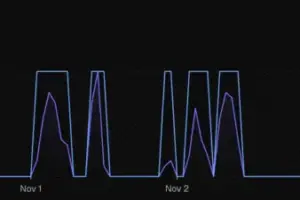
- October 5 – November 3: Layer3 Intel’s telemetry recorded persistent residential proxy activity originating from AS2650. During this 30-day window, proxy exit nodes traced back to the White House network on 26 distinct days, registering a total of 236 confirmed exits.
- Time-Of-Day Patterns: Forensic analysis indicated that the proxy activity was heavily concentrated during off-hours, primarily occurring in the evenings between 5:00 PM and midnight. This behavioral pattern strongly suggests that the affected devices were brought home by staffers or left active on corporate and personal networks outside of standard government monitoring environments.
- Scale of the Exposure: Investigators identified six distinct IP addresses within the White House network actively beaconing to external command-and-control and proxy orchestration servers.
The Infatica Connection and Russian Infrastructure
Of the 28 proxy services detected communicating through the White House network, Synthient identified active Windows 11 installations running Infatica.
Infatica operates by embedding software development kits (SDKs) into seemingly benign applications, including mobile apps and desktop browser extensions. When users install these applications—often marketed as free productivity tools, VPNs, or utility software—they unwittingly consent (via dense end-user license agreements) to share their internet bandwidth.
The historical context of Infatica’s leadership adds significant geopolitical weight to the findings. Infatica’s founder, Vladimir Fomenko, previously owned King Servers, a web hosting firm that served as the operational backbone for cyberattacks targeting state election administration databases in Arizona and Illinois in 2016. According to U.S. intelligence reports, those attacks were orchestrated by Russian state security services (GRU). While there is no direct evidence that the current White House proxy exposure was weaponized for a targeted state-sponsored operation, the presence of an infrastructure tied to historical Russian election interference on White House network peripherals has alarmed national security experts.
Supporting Context & Metrics: The Shadow Proxy Ecosystem
To understand how White House assets became entangled in a commercial proxy network, one must examine the mechanics of the modern residential proxy market.
How Residential Proxies Work
Residential proxies differ from traditional datacenter proxies because they utilize IP addresses assigned to regular residential broadband subscribers by Internet Service Providers (ISPs). Because these IPs look like legitimate home users rather than corporate data centers, they are heavily prized by threat actors, web scrapers, and fraudsters looking to bypass anti-bot defenses, commit ad fraud, or execute account takeover (ATO) attacks.
Proxy operators monetize these endpoints by paying app developers to bundle proxy SDKs into consumer software. Once installed, the user’s device acts as an unwitting relay node. When an external customer routes traffic through the proxy network, their requests pass through the user’s local machine, masking the customer’s true geographic location and identity.
A Cheap Gateway to High-Value Networks
The commercial accessibility of these networks makes them an unprecedented threat to enterprise and government security.
"Some of these resellers sell bandwidth for as low as 60 cents a gigabyte," said Ben Brundage, founder of Synthient, in an interview with KrebsOnSecurity. "That means for less than a dollar, you can gain access into some of the most confidential and trusted networks. The reseller ecosystem further enables this with any criminal able to buy access while skipping KYC [Know Your Customer] processes."
Layer3 Intel echoed this sentiment in their technical disclosure:
"This is public access. Anybody can obtain it by signing up to a public residential proxy service, paying a few dollars, and sending requests through it. We did not selectively target this network or try to make our probes exit from it. We caught this by chance, simply by requesting global rotating access through these services."
Systemic Vulnerabilities and Local Network Exploitation
Beyond the obvious risk of data exfiltration and traffic spoofing, residential proxy services have proven to be a frequent vector for direct network compromise.
- Late 2025: Security researchers discovered that cybercriminals were weaponizing widespread structural vulnerabilities inherent in residential proxy architectures. Attackers used proxy endpoints as a pivot point to scan local home and corporate subnets for vulnerable devices.
- January 2026: Synthient and other firms forced dozens of major proxy providers to rush out emergency patches after uncovering active campaigns (such as the "Kimwolf" botnet) that abused proxy nodes to seize administrative control over internal local network devices.
A Widespread Corporate and Governmental Scourge
The White House is far from an isolated casualty. The ubiquity of employee-owned devices bringing shadow IT into secure environments has created systemic vulnerabilities across critical infrastructure.
Data compiled by proxy-tracking service Spur during a January 2026 webinar revealed that residential proxy nodes were actively beaconing out from:
- Nearly 300 government-owned and operated networks.
- 318 utility companies.
- 166 healthcare organizations and hospitals.
- 141 banking and financial institutions.
Furthermore, enterprise security firm Infoblox reported earlier this year that an astonishing 65% of its corporate customer base had internal devices querying known residential proxy domains.
Official Statements and Accountability
As of press time, the White House has not officially responded to requests for comment regarding the Layer3 Intel and Synthient disclosures.
The silence from federal administration spokespersons underscores the complex jurisdictional and technical challenges agencies face when personal mobile devices, remote work laptops, and Bring Your Own Device (BYOD) policies intersect with high-security operational perimeters. Federal cybersecurity agencies, including the Cybersecurity and Infrastructure Security Agency (CISA), have increasingly warned against the dangers of untrusted third-party software on government-adjacent systems, yet enforcement against passive background monetizers remains difficult.
Future Outlook: Securing the Perimeter in an Era of Shadow Monetization
The exposure of White House network resources through commercial proxy nodes serves as a watershed moment for endpoint security. It demonstrates that traditional network perimeters—defined by firewalls and ASN allocations—are increasingly porous when pierced by software supply chain risks residing directly on user endpoints.
Security analysts emphasize that mitigating this threat requires a multi-layered approach:
- Aggressive Endpoint Detection and Response (EDR): Security teams must configure EDR and Mobile Device Management (MDM) platforms to actively scan for and block known residential proxy SDKs, proxy utilities, and unauthorized VPN browser extensions.
- Stricter App Whitelisting: Government agencies and high-security enterprises must strictly prohibit the installation of consumer-grade applications, free utilities, and ad-supported mobile software on any hardware connected to secure enterprise networks.
- Enhanced Know-Your-Customer (KYC) Regulations: Lawmakers and international regulators are facing mounting pressure to crack down on anonymous proxy brokers who operate without verifying the identity of their buyers or auditing the provenance of their IP exit pools.
Until systemic reforms are enacted across the commercial proxy industry, the boundary between the world’s most secure government networks and the global cybercriminal underground will remain dangerously blurred.