Federal Bureau of Investigation (FBI) agents have arrested a high-profile Canadian cybersecurity executive in Pennsylvania in connection with an escalating international investigation into the notorious ShinyHunters hacking collective. The suspect, identified in federal court records as 54-year-old Edward Dubrovsky—an industry veteran, author, and executive associated with Canadian cybersecurity and incident response firms—was taken into custody amid a major crackdown on cyber extortion intermediaries.
The arrest marks a critical inflection point in a high-stakes cyberwarfare drama. The ShinyHunters syndicate recently infiltrated the FBI’s own digital infrastructure, absconding with sensitive personnel dossiers detailing the units, specializations, medical histories, and psychiatric evaluations of thousands of federal agents.
According to multiple sources close to the investigation, Dubrovsky was apprehended while visiting Philadelphia to attend the annual Cyber Risk Summit—a premier industry event where his firm, CyberSteward, was listed as a primary sponsor. Court documents indicate that the case has been rapidly transferred to the Eastern District of Texas, which has quietly become the centralized command center for the federal government’s multi-jurisdictional offensive against ShinyHunters.
While federal authorities and the FBI have maintained a tightly guarded silence, the unfolding scandal exposes a murky intersection between the multi-million-dollar ransomware negotiation industry and the cybercriminal underground. With international arrests spanning the Netherlands, the United States, and beyond, the dragnet closing around ShinyHunters—and those who allegedly facilitate or advise on extortion payouts—signals a seismic shift in how law enforcement targets the ecosystem enabling modern cybercrime.
Detailed Chronology of the Arrest and Investigation
The events leading to Edward Dubrovsky’s arrest unspooled across international borders over a frantic, high-intensity 30-day window. The chronology highlights a coordinated global law enforcement strategy designed to systematically dismantle the infrastructure, leadership, and advisory networks supporting ShinyHunters.
Late September 2026: The Dutch Breakthrough
The current wave of arrests began in late September, when Dutch law enforcement authorities executed a high-profile raid, arresting Pepijn van der Stap, a reformed cybercriminal with historical ties to malicious syndicates. According to intelligence shared with KrebsOnSecurity, federal investigators subsequently seized numerous digital devices belonging to Van der Stap. The forensic extraction of data from these devices provided the FBI with a roadmap of communications, aliases, and financial pipelines connecting ShinyHunters operatives to corporate intermediaries operating in the legitimate cybersecurity space.
October 5 – October 7, 2026: The Trap in Philadelphia
While the FBI was poring over forensic data from the Netherlands, Edward Dubrovsky traveled to Philadelphia, Pennsylvania, to participate in the NetDiligence Cyber Risk Summit held at the Loews Philadelphia Hotel. Dubrovsky, a prominent figure in the Canadian cybersecurity community and an outspoken advocate for structured ransomware advisory services, was slated to network with industry peers and insurance executives.
Unbeknownst to Dubrovsky, federal agents were closing in. On October 8, 2026—just one day after the summit concluded—law enforcement executed an arrest warrant, taking Dubrovsky into custody. Federal court records filed under the slightly misspelled name "Edward Dobrovsky" reveal preliminary charges of conspiracy to threaten to impair the confidentiality of information with the intent to extort money, alongside charges of interference with commerce by threats.
October 8 – October 9, 2026: Court Filings and Jurisdictional Shifts
Immediately following his arrest, Dubrovsky was booked into a federal detention facility in Philadelphia, as logged by the U.S. Bureau of Prisons inmate locator. However, the legal proceedings underwent an abrupt geographic pivot. On October 9, court filings indicated that the prosecution had been formally transferred to the U.S. District Court for the Eastern District of Texas. Sources familiar with the federal docket confirm that the Eastern District of Texas has been designated as the central repository and command center for all major indictments and investigative leads related to the ShinyHunters probe.

As of press time, Dubrovsky remains detained and has not yet retained legal counsel or been assigned a public defender by the court. Representatives for CyberSteward have not responded to requests for comment, while Cypfer—a separate Canadian cybersecurity firm where Dubrovsky previously served as a managing director prior to his November 2025 resignation—issued clarifying statements distancing themselves from his current professional activities.
Supporting Context & Metrics: The Anatomy of ShinyHunters
To understand the gravity of Dubrovsky’s arrest and the FBI’s aggressive posture, one must examine the operational footprint of ShinyHunters and the staggering financial scale of the modern cyber extortion economy.
Modus Operandi and Financial Impact
ShinyHunters has historically operated by exploiting corporate vulnerabilities—predominantly through sophisticated phishing campaigns, credential stuffing, and the compromise of Software-as-a-Service (SaaS) environments. Once inside a corporate network, the group siphons vast quantities of proprietary data, intellectual property, and customer records. Rather than deploying traditional file-encrypting ransomware, the group relies primarily on pure-play data exfiltration and extortion: they threaten to leak sensitive corporate assets publicly unless steep cryptocurrency demands are satisfied.
According to internal FBI metrics, ShinyHunters has proven exceptionally prolific and destructive. Federal estimates indicate that the syndicate has successfully extorted more than $70 million from corporate and institutional victims during the 2026 calendar year alone.
The Breach of the FBI
The conflict between ShinyHunters and federal law enforcement escalated from a standard criminal investigation into a personal crusade when the hacking group successfully breached the FBI’s own online recruitment portal.
Following the late-September arrest of Pepijn van der Stap by Dutch authorities, a core ShinyHunters administrator operating under the alias "Rey" assumed direct operational control of the syndicate. In a brazen display of defiance, Rey began taunting federal investigators online, leaking a cache of compromised FBI data. The stolen records included deeply sensitive dossiers on thousands of active-duty and prospective federal agents, detailing their military or law enforcement units, specialized operational training, and confidential medical and psychiatric evaluations.
The Capture of "Rey"
The FBI’s retaliation was swift and international in scope. Working in tandem with global intelligence partners, investigators unmasked the hacker operating as "Rey." Reports published by Reuters revealed that the mastermind behind the agency’s humiliation was a teenager identified as Saif Al-din Khader.
Khader was apprehended shortly after leading an extortion campaign targeting a navigation and digital aviation unit that had been divested by aerospace giant Boeing in late 2025. Following his detention, Khader reportedly began cooperating with federal authorities, providing investigators with critical intelligence that accelerated the subsequent targeting of corporate fixers and negotiation intermediaries—culminating in the arrest of Edward Dubrovsky.
Official Statements and Industry Fallout
The intersection of law enforcement, corporate cybersecurity, and criminal syndicates has sent shockwaves through the global incident response community.

FBI Leadership and Institutional Silence
Official public disclosures regarding the operation remain tightly controlled. FBI Director Kash Patel issued a brief, high-level statement via social media confirming the apprehension of a Canadian national in Pennsylvania linked to the ShinyHunters conspiracy, though he initially withheld specific names. When approached by journalists for comment regarding Dubrovsky’s specific role, corporate affiliations, and the Texas court transfer, FBI spokespersons declined to elaborate, citing an ongoing, active investigation.
The Controversy Over Ransomware Advisory and Negotiation
Dubrovsky’s arrest has cast a glaring, uncomfortable spotlight on the multi-million-dollar ecosystem of ransomware negotiators, cyber insurance adjusters, and extortion advisors. Dubrovsky is a recognized authority in the field, having authored the 252-page professional text Cyber Extortion Strategic Response.
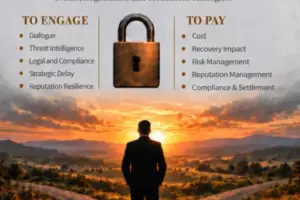
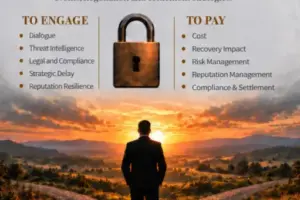
The book, marketed heavily on professional platforms like Amazon and LinkedIn, purports to guide corporate executives through the complex legal, ethical, and tactical decisions required during a cyber crisis. An excerpt from the text highlights a central thesis of the industry:
"At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
While firms like Cypfer and CyberSteward position these services as legitimate, risk-mitigated advisory frameworks designed to protect victimized organizations from catastrophic data leaks, federal prosecutors appear to be drawing a harder line. Investigators are increasingly scrutinizing whether certain advisory firms cross the legal threshold from compliance-driven negotiation into active conspiracy, facilitation of extortion payments, or the provision of material support to designated cybercriminal enterprises.
Future Outlook: What Lies Ahead
As federal prosecutors in the Eastern District of Texas prepare their formal indictments, the legal and operational ramifications of this case will likely redefine the boundaries of the cybersecurity industry.
- Expansion of the Indictment Net: Sources close to the investigation have indicated that Dubrovsky may not be the last private-sector executive facing criminal charges. Federal investigators are actively reviewing the digital devices, communications logs, and financial transactions of other high-profile firms specializing in ransomware negotiation and incident response.
- Regulatory Crackdown on Extortion Payments: The revelation that extortion intermediaries may be operating too closely with syndicates like ShinyHunters is expected to prompt renewed calls from lawmakers for stricter federal regulations on ransomware payments, mandatory breach disclosures, and tighter oversight of cyber insurance payouts.
- The Erosion of Anonymity in Cybercrime: The rapid unmasking and apprehension of core operatives—from Dutch facilitators like Van der Stap to teenage administrators like Saif Al-din Khader, and now corporate consultants like Dubrovsky—demonstrates a devastatingly effective whole-of-government approach. Cross-border cooperation, advanced digital forensics, and cooperative flips are effectively closing the net on the untouchable elite of the cybercrime underworld.
As this fast-moving story continues to develop, legal experts anticipate high-stakes pretrial motions regarding jurisdiction, the handling of sealed federal indictments, and the broader implications for corporate crisis management professionals operating globally.