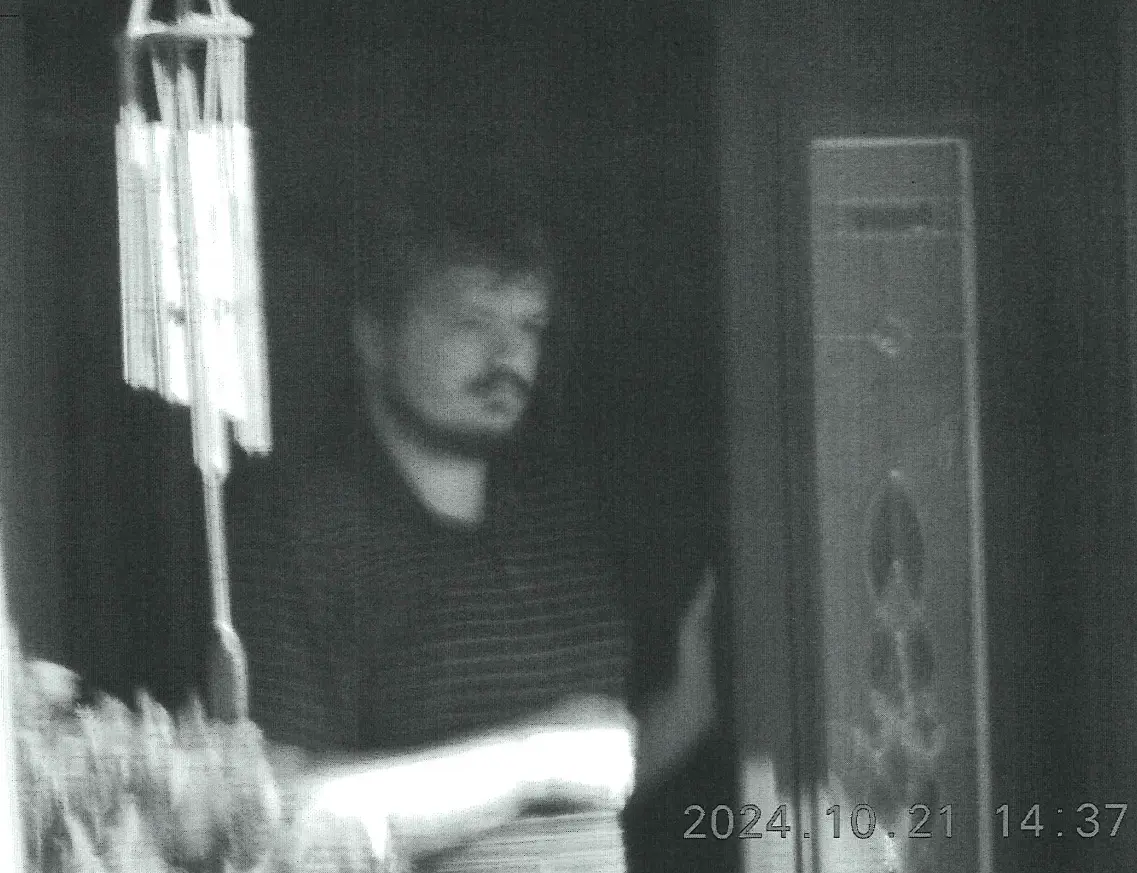
Federal Bureau of Investigation (FBI) agents have apprehended a prominent Canadian cybersecurity executive in Pennsylvania, marking a dramatic escalation in an ongoing, high-stakes international investigation into the notorious ShinyHunters cybercrime syndicate. The arrest of the executive—identified in federal court records as Edward Dubrovsky—comes on the heels of a massive and deeply embarrassing data breach that saw the hacking collective compromise sensitive, confidential files belonging to thousands of federal law enforcement agents.
Dubrovsky, who has built a career advising major corporations on ransomware mitigation, crisis management, and cyber extortion strategies, was taken into custody in early October while attending a major industry conference in Philadelphia. Court documents indicate he faces serious federal charges, including conspiracy to commit cyber extortion and interference with commerce by threats.
The investigation has rapidly expanded into a multi-jurisdictional dragnet. Law enforcement partners in Europe and North America have launched parallel sweeps, seizing electronic devices, detaining key syndicate leaders, and scrutinizing the complex, murky ecosystem of ransomware negotiation firms. As federal authorities centralize the prosecution out of an FBI field office in Texas, this unfolding scandal exposes the precarious and sometimes ethically ambiguous intersections where corporate incident response firms, cyber insurance providers, and ruthless extortion syndicates meet.
Detailed Chronology of Events
The sequence of events leading up to Dubrovsky’s arrest reveals a rapidly moving federal operation driven by intense international cooperation and severe pressure following a major breach of U.S. national security infrastructure.
The October Summit and the Arrest in Pennsylvania
Federal agents moved in to arrest Edward Dubrovsky during his visit to Philadelphia for the prominent Cyber Risk Summit, held at the Loews Philadelphia Hotel from October 5 to October 7, 2026. Dubrovsky, a well-known figure in the Canadian cybersecurity landscape, was attending the conference alongside representatives from CyberSteward, a security firm he is currently associated with.
According to federal court records filed in Pennsylvania, Dubrovsky was formally charged under a slightly misspelled surname—Dobrovsky—on October 8. The initial charges accuse him of "conspiracy to threaten to impair the confidentiality of information with the intent to extort money" and "interference with commerce by threats." While several core documents, including the primary arrest complaint, remain sealed under judicial order, an initial summary of the charges was indexed on public dockets via CourtListener.
Following his initial detainment and brief holding at a federal facility in Philadelphia, legal documentation filed on October 9 directed the transfer of the case to the U.S. District Court for the Eastern District of Texas. Sources close to the investigation confirm that the Eastern District of Texas has now become the central command hub for the broader federal prosecution of the ShinyHunters network.
The European Connection: The Raid on Pepijn van der Stap
Dubrovsky’s arrest does not exist in a vacuum; it is the latest domino to fall in an aggressive, coordinated crackdown on the infrastructure supporting modern cyber extortion. Weeks prior to the Philadelphia arrest, Dutch law enforcement executed raids resulting in the apprehension of Pepijn van der Stap, a reformed hacker and figure tied directly to the ShinyHunters investigation.
According to federal and intelligence sources, FBI investigators have spent weeks meticulously combing through digital devices and data hard drives seized during the Dutch raids. The intelligence recovered from van der Stap’s hardware provided the critical breadcrumbs that connected international ransomware negotiation entities to the inner workings of the extortion enterprise. Analysts suggest that the trove of data has paved the way for additional charges against principals and executives at other boutique firms specializing in ransomware negotiation and payout facilitation.
The Rise and Fall of "Rey"
The urgency of the federal response was compounded exponentially by the brazen actions of the ShinyHunters group following van der Stap’s arrest. Immediately after the Dutch police operation, a prominent member of the syndicate operating under the handle "Rey" assumed operational control of the group.
In a display of unprecedented audacity, Rey began taunting federal authorities online regarding a devastating breach of the FBI’s own online recruitment portal. The stolen data trove included highly sensitive, non-public details regarding thousands of federal agents, encompassing their specific operational units, specialized skill sets, and deeply personal medical and psychiatric evaluations.
The reign of the teenage mastermind was short-lived. Reuters reported that Rey—subsequently identified as a teenager named Saif Al-din Khader—was detained by authorities and is currently cooperating with FBI investigators. Just prior to his apprehension, investigative reports detailed how Khader and his associates attempted to extort a major navigation and digital aviation unit recently divested by aerospace giant Boeing in late 2025.
Supporting Context & Metrics: The Anatomy of ShinyHunters
To understand the gravity of the federal investigation, one must examine the operational blueprint of the ShinyHunters hacking group and the lucrative, high-stakes market of ransomware negotiation.
Modus Operandi and Financial Impact
ShinyHunters has historically distinguished itself through sophisticated phishing campaigns, credential theft, and relentless exploitation of corporate accounts across Software-as-a-Service (SaaS) providers. Once inside a corporate network, the group exfiltrates vast repositories of proprietary and personal data, establishing heavy leverage before issuing devastating extortion demands. Victims who refuse to pay typically see their intellectual property, customer databases, or internal communications leaked indiscriminately online.
Federal estimates underscore the staggering profitability of these operations. According to official FBI metrics, the ShinyHunters syndicate alone has successfully extorted more than $70 million from corporate and institutional victims globally over the course of the year.
The Complex Ecosystem of Ransomware Negotiation
The arrest of an executive from a firm specializing in ransomware advisory sheds light on a shadowy multi-million-dollar industry. Companies targeted by cyber extortionists frequently retain specialized negotiation firms to manage communications, verify the authenticity of stolen data claims, evaluate operational risks, and, when deemed necessary, facilitate cryptocurrency ransom payments.
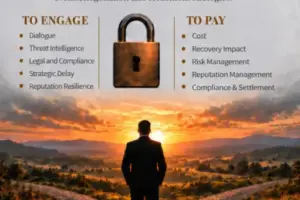
Edward Dubrovsky is an established voice in this niche, having authored the 252-page professional guide Cyber Extortion Strategic Response. The book, marketed as a manual to help organizations navigate post-breach crises, highlights a critical distinction in modern cybersecurity doctrine:
"At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
However, federal prosecutors appear to believe that certain actors within the advisory ecosystem crossed the fine line separating third-party negotiation from active criminal conspiracy, facilitation, or obstruction of justice.
Official Statements and Institutional Responses
Official communication surrounding the arrests has been tightly controlled, reflecting the sensitive nature of an active counter-intelligence and criminal investigation that directly compromised the FBI’s internal personnel files.
In the immediate wake of the Pennsylvania operation, FBI Director Kash Patel released a brief, targeted statement via social media on X (formerly Twitter) acknowledging the apprehension of a Canadian national linked to the ShinyHunters probe, though initial disclosures withheld specific names to protect the integrity of the pending legal proceedings.
Corporate entities linked to the unfolding drama have moved swiftly to distance themselves from the fallout. Dubrovsky’s professional affiliations have experienced intense public scrutiny:
CyberSteward: The Canadian security firm, where Dubrovsky was actively working and slated to present at the Philadelphia risk summit, has faced immediate inquiries from media outlets regarding the executive’s status.
Cypfer: Following initial media reports identifying Dubrovsky as a founder or co-founder of Cypfer, a corporate spokesperson issued an official clarification. Cypfer management asserted that Dubrovsky was never a founder, but rather served as a managing director prior to his resignation in November 2025.
As of press time, federal prosecutors in the Eastern District of Texas have declined to provide exhaustive commentary on the specifics of the indictment, and spokespeople for the U.S. Department of Justice maintain that additional details will be unsealed as the case progresses through the federal court system. Court records indicate that Dubrovsky has not yet retained private counsel, nor has the court formally appointed a public defender to represent him.
Future Outlook: What Lies Ahead
The arrest of a veteran cybersecurity executive on federal extortion charges signals a paradigm shift in how law enforcement approaches the cybercrime underground. For years, the boundary between legal incident response advisory and illicit facilitation remained a gray area, tolerated as a necessary evil in the face of rampant corporate ransomware infections. By targeting executives who operate in these spaces, the Department of Justice is sending an unambiguous warning shot to the entire cybersecurity consultancy sector.
Moving forward, several critical developments are anticipated:
Unsealing of Indictments: As the legal proceedings transition fully to the Eastern District of Texas, defense motions and scheduled preliminary hearings are expected to shed light on the specific evidentiary thresholds used by federal prosecutors to connect negotiation advisories to criminal conspiracy.
Expansion of the Indictment Wave: Intelligence sources strongly indicate that Dubrovsky will not be the last corporate executive targeted. Additional arrests of principals operating within boutique ransomware negotiation and mediation firms are anticipated as the FBI parses the hardware seized from both European raids and recent domestic sweeps.
Internal Security Overhauls at Federal Agencies: The catastrophic compromise of the FBI’s own recruitment portal—yielding medical, psychiatric, and operational data on thousands of federal agents—has forced a comprehensive security audit of all internal federal IT systems and human resource pipelines.
This remains a rapidly evolving, fluid news story. Further updates, institutional responses, and court filings will be documented as new details emerge from federal dockets and investigative sources.