By Investigative Staff
Published: October 2026
Executive Overview
In a dramatic escalation of one of the most high-profile cybercrime investigations in recent history, federal law enforcement agents have arrested a prominent Canadian cybersecurity executive in connection with the notorious ShinyHunters hacking collective. The arrest—unfolded in Pennsylvania and subsequently corroborated by multiple high-level intelligence and security sources—shines a harsh, unwelcome spotlight on the gray-market ecosystem of ransomware negotiations, incident response firms, and digital extortion advisory services.
The suspect, identified in federal court records as 54-year-old Edward Dubrovsky, is a veteran cybersecurity professional, a published author on ransomware strategy, and an executive linked to prominent Canadian security startups. According to documents indexed via CourtListener and insights provided to KrebsOnSecurity, Dubrovsky stands accused of cyber extortion and conspiracy. His apprehension marks a monumental pivot in the U.S. government’s war against ShinyHunters, a cybercrime syndicate that recently humiliated federal authorities by breaching an FBI online portal and making off with sensitive personnel data, unit assignments, and psychiatric records of thousands of agents.
While the core criminal complaint and several key evidentiary documents remain strictly sealed by the court, the fallout from Dubrovsky’s arrest extends far beyond an individual indictment. It exposes deep fractures in the corporate incident response industry, where the line between legitimate negotiation advisory and illicit collusion with criminal enterprises is increasingly scrutinized by federal prosecutors. As control of the multi-jurisdictional investigation centralizes within an FBI field office in Texas, investigators are poring over digital evidence seized internationally, signaling that Dubrovsky may be just the first domino to fall among third-party ransomware intermediaries.
Detailed Chronology of Events
The convergence of events leading to Dubrovsky’s arrest reads like a masterclass in modern international cyber-investigation, weaving together conferences in Philadelphia, law enforcement raids in Europe, and digital taunts exchanged across social media.
The Cyber Risk Summit and the Philadelphia Trap
The sequence of events culminated during the first week of October 2026. According to sources close to the investigation, Dubrovsky had traveled from Canada to Pennsylvania to attend the annual Cyber Risk Summit, hosted at the Loews Philadelphia Hotel between October 5 and October 7. The event—a major gathering for cyber insurance professionals, risk assessors, and incident responders—featured several high-profile sponsors. Among the elite backers of the conference was Cypfer, a Canadian security firm specializing in ransomware negotiations, alongside CyberSteward, another boutique security entity with which Dubrovsky was actively collaborating.
Unbeknownst to conference attendees, federal agents had been tracking Dubrovsky’s movements. On October 8—just one day after the conclusion of the Philadelphia summit—FBI agents moved in and arrested Dubrovsky. Federal court records filed in Pennsylvania reflect his booking under a slight variation of his surname (Dobrovsky), citing severe charges related to interference with commerce by threats and conspiracy to impair the confidentiality of data for financial extortion.
From Philadelphia to the Eastern District of Texas
Immediately following his capture, Dubrovsky was processed and temporarily housed at a federal detention facility in Philadelphia, as verified by the U.S. Bureau of Prisons inmate locator. However, the legal trajectory of the case shifted almost overnight.
On October 9, court filings indicated that the case was formally ordered to be transferred to the U.S. District Court for the Eastern District of Texas. Sources indicate that this federal district has become the strategic epicenter for the sprawling, nationwide investigation into ShinyHunters. As of writing, Dubrovsky remains without formal retained counsel, and the court has yet to assign a public defender to his docket.

Supporting Context & Metrics: The Anatomy of the ShinyHunters Threat
To understand the gravity of Dubrovsky’s arrest, one must examine the operational blueprint and recent rampage of the ShinyHunters collective.
Who is ShinyHunters?
ShinyHunters is not a traditional, monolithic ransomware gang that deploys custom encryptors across corporate networks. Instead, the group operates primarily as an elite data-theft and extortion cartel. Their standard methodology relies heavily on targeted phishing campaigns, compromised corporate credentials, and the exploitation of vulnerabilities within software-as-a-service (SaaS) environments. Once inside a corporate cloud infrastructure, they siphon massive repositories of proprietary data, intellectual property, and customer records, subsequently threatening to leak the information publicly unless exorbitant cryptocurrency ransoms are paid.
According to internal intelligence metrics cited by the FBI, ShinyHunters has been extraordinarily prolific and destructive, successfully extorting more than $70 million from corporate and institutional victims globally over the course of 2026 alone.
The European Connection: Pepijn van der Stap
The dragnet tightening around ShinyHunters began to constrict significantly in September 2026, when Dutch law enforcement authorities executed a series of targeted raids, arresting Pepijn van der Stap, a reformed cybercriminal whose digital infrastructure was allegedly co-opted or utilized by the syndicate. The forensic seizure of van der Stap’s hardware provided FBI investigators with a trove of communication logs, cryptocurrency wallet addresses, and operational metadata that connected international intermediaries directly to the core leadership of ShinyHunters.
The FBI Data Breach and the Rise of "Rey"
The audacity of ShinyHunters reached a fever pitch in the wake of van der Stap’s arrest. A faction leader within the group operating under the pseudonym "Rey" assumed operational control and launched a public campaign of psychological warfare against U.S. law enforcement.
In an unprecedented breach, ShinyHunters managed to infiltrate an online recruitment and vetting portal belonging to the FBI itself. The stolen cache included deeply sensitive background information on thousands of active-duty special agents, detailing their specific unit assignments, operational specializations, and—most damagingly—confidential medical and psychiatric evaluations. Rey utilized this stolen intelligence to taunt FBI leadership publicly across social media channels, posting screenshots and daring federal agents to shut down their infrastructure.
The bravado was short-lived. Following cooperative intelligence-sharing initiatives, international law enforcement and Reuters-backed reporting revealed that "Rey" was actually a teenager named Saif Al-din Khader. Khader was subsequently detained and began cooperating with federal investigators. Prior to his apprehension, Khader and his cell had turned their sights on high-value corporate targets, including an aggressive attempt to extort a digital aviation and navigation unit recently divested by aerospace giant Boeing in late 2025.
Official Statements and Industry Fallout
The arrest of a senior cybersecurity executive on charges of aiding or conspiring with cyber extortionists has sent shockwaves through the global incident response and cyber insurance industries.
Silence from the Top
Official channels have remained remarkably tight-lipped regarding the specifics of Dubrovsky’s alleged collusion. FBI Director Kash Patel acknowledged the general apprehension of a Canadian national tied to the ShinyHunters probe via social media, but neither his statement nor subsequent briefings from the Bureau elaborated on how an executive from a reputable security firm intersected with a criminal hacking cartel. The FBI formally declined to comment on ongoing investigative specifics.

Corporate Distancing and the Gray Market of Negotiations
The fallout has hit Canadian security firms hard, forcing immediate public relations damage control. Dubrovsky’s professional footprint shows deep ties to Cypfer, where LinkedIn records previously identified him as a co-founder and managing director. However, in an urgent statement issued on October 10, a Cypfer spokesperson forcefully corrected the public record, clarifying that Dubrovsky was never a founder or co-founder of the firm, but rather served in a managerial capacity until his resignation in December 2025.
Following his departure from Cypfer, Dubrovsky aligned himself with CyberSteward, another Canadian security firm and sponsor of the Philadelphia Cyber Risk Summit. Just one month prior to his arrest, Dubrovsky had posted enthusiastically on LinkedIn about attending the summit to discuss "strategy and compliant driven coercive (ransomware, extortion) advisory, negotiations and settlement services."
Ironically, Dubrovsky is also the author of Cyber Extortion Strategic Response, a 252-page textbook published to guide organizations through the complex labyrinth of ransomware incidents. In promotional material for the book, Dubrovsky wrote:
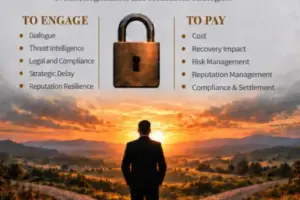
"At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
Federal prosecutors in Texas now face the formidable task of proving where legitimate "tactical engagement" ended and criminal conspiracy, extortion facilitation, or money laundering allegedly began.
Future Outlook: A Turning Point for Ransomware Intermediaries
Dubrovsky’s arraignment and the ongoing transfer of his case to the Eastern District of Texas signal a structural shift in how law enforcement views the peripheral ecosystem of cybercrime. For years, the billion-dollar ransomware negotiation industry has operated in a legal and ethical twilight zone. Companies facing catastrophic data leaks routinely hire third-party advisory firms to quietly handle threat actors, vet decryption tools, and structure cryptocurrency payments—often without direct law enforcement oversight or interference.
According to sources close to the KrebsOnSecurity investigation, federal prosecutors are aggressively expanding their scope. Investigators are currently analyzing forensic evidence harvested from devices seized during the Dutch police raids and the subsequent U.S. arrests. Legal experts anticipate that Dubrovsky will not be the last corporate executive or "ransom broker" to face federal indictments.
As this fast-moving, high-stakes investigation continues to unfold, it threatens to fundamentally reshape the incident response industry. Security firms will likely face rigorous compliance audits, heightened scrutiny regarding their communication channels with threat actors, and a chilling realization that assisting cyber extortionists—even under the guise of corporate advisory and risk mitigation—can land executives on the wrong side of a federal indictment.
This is a developing story. Further updates, court filings, and official statements will be appended as new information becomes available.