Executive Overview
In a decisive maneuver targeting the financial arteries of illicit global cybercrime and state-sponsored sanctions evasion, the United Kingdom has levied sweeping economic sanctions against Cryptomus, a notorious cryptocurrency payment processor. For years, Cryptomus has operated as a chameleonic entity—shifting names, dodging regulatory oversight, and spawning parallel operations—to facilitate billions of dollars in illicit transactions.
According to leading blockchain intelligence firms and investigative journalists, the platform has functioned as a central clearinghouse for ransomware gangs, narcotics traffickers, darknet market operators, and cybercrime services. Crucially, these operations have played a vital role in helping the Russian government and associated financial institutions circumvent sweeping international economic restrictions tied to the war in Ukraine.
The U.K. Foreign, Commonwealth & Development Office action, formally executed on October 8, freezes all domestic assets linked to Cryptomus and blocks British citizens and entities from engaging in any commercial or virtual transactions with the platform. Alongside Cryptomus, the U.K. government targeted several allied virtual payment services, including VexPay, TokenSpot, and the Tsunami Payments service.
This milestone enforcement action marks a significant escalation in Western efforts to dismantle the underground financial infrastructure sustaining Russia’s wartime economy. Furthermore, security experts emphasize a historic precedent: this appears to be the first known instance where a "Five Eyes" intelligence-sharing nation (comprising Australia, Canada, New Zealand, the U.K., and the U.S.) has officially sanctioned a cryptocurrency platform incorporated within the borders of another Five Eyes jurisdiction.
Detailed Chronology: From Certa Payments to Heleket
The operational history of Cryptomus is a masterclass in corporate evasion, regulatory arbitrage, and structural reinvention. To understand how the platform managed to evade conventional enforcement for years, it is necessary to trace its trajectory from an obscure startup to a multi-billion-dollar illicit financial hub.
The Emergence of Certa Payments and Cryptomus (2022)
Emerging onto the digital landscape in 2022, the platform initially operated under corporate banners such as Certa Payments and Xeltox Enterprises. Behind a polished web facade, it positioned itself as a modern payment gateway for online merchants, quickly becoming the preferred processing engine for dozens of Russian cryptocurrency exchanges and underground sites peddling cybercrime-as-a-service (CaaS) products.
Canadian Scrutiny and Record Fines (October 2025)
As transaction volumes ballooned, international watchdogs began taking notice. Investigative reporting by Krebs on Security in late 2024 revealed that Cryptomus shared a physical address in Vancouver, Canada, with dozens of other foreign currency dealers and money transfer businesses—none of which maintained an actual physical presence at the location.
The web of illicit activity finally caught up with the company in October 2025, when Canadian regulatory authorities levied a record-shattering CAD $176 million fine against Cryptomus for egregious violations of anti-money laundering (AML) and know-your-customer (KYC) frameworks.
However, rather than buckling under the financial penalty, the platform initiated a playbook of deflection. Cryptomus formally appealed the Canadian fine while simultaneously launching a parallel, no-KYC processing service dubbed "Heleket."
The Rebranding to Heleket and the Crypto Crackdown
Faced with mounting pressure, the core operators rebranded the enterprise as Heleket, attempting to distance the new storefront from the toxic reputation of the Cryptomus moniker. Despite public denials from Telegram support agents—who routinely insisted to inquirers that Heleket had no affiliation with Cryptomus—blockchain analysts quickly unmasked the continuity of the underlying infrastructure, wallet architecture, and backend personnel.
The U.K. Sanctions Hammer Drops (October 2026)
Recognizing that administrative fines and uncollectible monetary judgments were insufficient to halt operations, the British government stepped in. On October 8, 2026, the U.K. issued strict sanctions freezing Cryptomus’s operational capabilities within its jurisdiction. Within hours of the announcement, Telegram support bots for both Cryptomus and Heleket began broadcasting emergency notices to users, stating that the platforms were suddenly and indefinitely unable to process transactions.

Supporting Context & Metrics: The Scale of Illicit Flows
The true economic footprint of Cryptomus and its spin-offs is staggering. Far from being a niche player handling fringe transactions, the platform grew into a systemic risk within the global cryptocurrency ecosystem.
Tracing the Billions: TRM Labs and Chainalysis Data
In April 2026, blockchain analysis firm TRM Labs published a comprehensive intelligence brief revealing that Cryptomus had processed more than $7 billion in transactions since its inception in 2022. This staggering volume was not confined to standard e-commerce; TRM Labs identified significant transaction flows associated with some of the darkest corners of the internet, including:
- Distributors of child sexual abuse material (CSAM).
- State-aligned and independent terrorist financing networks.
- International human trafficking rings.
- Prolific ransomware syndicates demanding multi-million-dollar cryptocurrency payouts.
Data compiled by Chainalysis further contextualized the scale of the operation, particularly its integration into Russia’s wartime financial networks. In an October 8 blog post analyzing the U.K. sanctions, Chainalysis noted that Cryptomus and Heleket had emerged as primary payment conduits for illicit activity, surpassing traditional cryptocurrency mixers in total illicit funds received across tracked categories.
At its peak in late 2025, the number of distinct illicit counterparties interacting with the platform surged to more than 900 in a single month.
The KYC Paradox and Volume Compression
Interestingly, blockchain researchers observed a temporary contraction in Cryptomus’s transaction volumes prior to its full-scale collapse. This dip occurred after the platform briefly instituted rudimentary "Know Your Customer" (KYC) rules in an effort to appease international regulators.
However, rather than cleaning up its client base, the platform’s response to the Canadian enforcement action was to spin up Heleket as an unverified, no-KYC sanctuary. This pivot allowed ransomware operators and darknet vendors to seamlessly redirect their payment streams, maintaining high illicit transaction volumes until the U.K. sanctions effectively severed their access to Western financial liquidity.
Official Statements and Expert Analysis
The dismantling of Cryptomus has drawn praise from the cybersecurity and blockchain intelligence communities, who have long advocated for coordinated international sanctions over administrative monetary fines.
The Distinction Between Fines and Sanctions
Richard Sanders, a prominent blockchain analyst and investigator who spent months painstakingly mapping out Cryptomus’s payment infrastructure and interacting directly with its network of customers, emphasized the legal and operational differences between the penalties imposed by Canada and those enacted by the United Kingdom.
"A fine doesn’t stop a cryptocurrency payment processor from processing payments," Sanders wrote in a widely shared professional analysis. "Sanctions kill the operation. The distinction matters."
Sanders pointed out that while Canada’s CAD $176 million penalty sent a powerful regulatory message, it was ultimately unenforceable and uncollectible given the shell-company architecture of the enterprise. By contrast, the U.K. asset freeze and business prohibition legally binds any entities operating within British jurisdiction, effectively cutting off the platform’s liquidity and forcing its operational infrastructure offline.
Disrupting Wartime Supply Chains
Chainalysis echoed these sentiments in its official advisory, emphasizing that the action against Cryptomus, VexPay, TokenSpot, and Tsunami Payments underscores a growing recognition by Western governments that cybercrime and state-sponsored sanctions evasion are deeply intertwined.

By choking off the virtual payment processors that convert illicit cryptocurrency into usable fiat currency for Russian entities, international regulators are systematically dismantling the financial scaffolding supporting foreign aggression and transnational organized crime.
The Phantom Regulator: Tracing the Corporate Fiction
Perhaps the most bizarre and illuminating aspect of the Cryptomus investigation is the origin of its corporate legitimacy. How did a platform facilitating billions of dollars in ransomware and darknet payments secure the authority to operate international financial services in the first place?
The Western Sahara Connection
An investigative deep dive into the corporate paperwork behind Cryptomus uncovered a labyrinthine web of shell companies rooted in geopolitical fiction.
The sole shareholder of Cryptomus’s initial parent company, Certa Payments, was identified as a 25-year-old Ukrainian woman. Alongside her leadership role at Certa, she served as the head of several other entities, including the WS Management and Advisory Corporation.
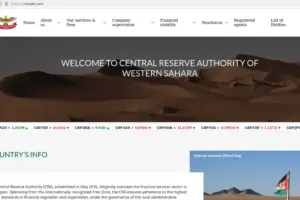
This corporation marketed itself aggressively as an elite, exclusive regulatory body. Specifically, it claimed to hold sole authority for issuing and overseeing regulatory licenses for cryptocurrency exchanges, foreign exchange brokers, and online gaming businesses incorporated within the Western Sahara—a disputed region in northwest Africa that is not universally recognized as a sovereign nation.
Phony Regulators and Shared Servers
The regulatory front organization operated primarily through the website crasadr.com, which purported to represent the Central Reserve Authority of the Western Sahara. The site offered prospective financial applicants streamlined assistance with offshore bank account setup, online gambling licenses, and crypto-brokerage authorization.
Technical infrastructure analysis conducted during the investigation revealed striking overlaps between these entities. One of Certa Payments’ former domains (certa.website) shared a web server with no fewer than 12 other domains, including rasd-state.ws—the designated digital portal for the fake Western Sahara monetary authority.
This reliance on unrecognized jurisdictions and phantom regulators highlights the sophisticated mechanisms modern cybercrime syndicates employ to mimic legitimate financial institutions, shielding illicit operations behind a veneer of bureaucratic legitimacy until international law enforcement pierces the corporate veil.
Future Outlook: The Death Knell for Offshore Crypto Gateways?
The coordinated pressure resulting in the shutdown of Cryptomus and Heleket signals a pivotal turning point in cryptocurrency regulation and law enforcement. As blockchain analytics firms develop increasingly sophisticated attribution capabilities, the days of hiding behind revolving corporate identities, phantom regulatory bodies, and no-KYC parallel services are rapidly drawing to a close.
Yet, the saga of Cryptomus also illustrates the resilience of underground financial networks. As long as lucrative markets exist for ransomware monetization, darknet trade, and state-sponsored sanctions evasion, bad actors will continue to seek out vulnerable regulatory corridors.
Nevertheless, the U.K.’s decisive action has established a new benchmark for cross-border enforcement. By moving beyond unenforceable fines and deploying crippling economic sanctions against virtual payment hubs, Western governments have demonstrated that the infrastructure supporting cybercrime and wartime financial evasion can be successfully dismantled—permanently altering the risk calculus for illicit crypto operators worldwide.