Executive Overview
Federal Bureau of Investigation (FBI) agents have arrested a high-profile Canadian cybersecurity executive in Pennsylvania, marking a dramatic escalation in the multi-jurisdictional manhunt for the notorious cybercrime syndicate known as ShinyHunters. The suspect, identified through federal court records and industry sources as Edward Dubrovsky, is a veteran security professional, author, and specialist in ransomware response and extortion negotiations.
The arrest took place amidst a turbulent period for U.S. federal law enforcement. The ShinyHunters hacking collective recently dealt a severe blow to national security by breaching FBI infrastructure, making off with sensitive personnel data—including operational unit assignments, specializations, and confidential medical and psychiatric records—affecting thousands of special agents.
According to multiple sources close to the investigation, Dubrovsky was apprehended while visiting Philadelphia to attend the high-profile Cyber Risk Summit. Federal filings show he faces severe charges, including conspiracy to threaten the impairment of data confidentiality to extort money, and interference with commerce through threats. The case has since been transferred to the Eastern District of Texas, which has rapidly become the centralized hub for the Justice Department’s comprehensive assault on the ShinyHunters ecosystem.
As international law enforcement agencies close in on the syndicate’s core operators, negotiators, and affiliates, this unfolding scandal exposes the murky, high-stakes intersection where corporate incident response firms meet the shadowy underworld of cyber extortion.
Detailed Chronology of Events
The events leading up to Dubrovsky’s arrest trace a winding path across international borders, digital confrontations, and specialized security conferences.
The Trap Springs in Philadelphia
Between October 5 and October 7, 2026, the Loews Philadelphia Hotel hosted the annual Cyber Risk Summit organized by NetDiligence. The event brought together leading figures in the cyber insurance, risk mitigation, and incident response sectors. Among the prominent sponsors was CyberSteward, a Canadian security firm with which Dubrovsky was closely associated, having previously served as a managing director at Cypfer, another major Canadian player in the ransomware negotiation space (though Cypfer later clarified that Dubrovsky resigned in November 2025 and was not a founding member, as his LinkedIn profile had suggested).
Unbeknownst to conference attendees, federal authorities had been tracking Dubrovsky. On October 8—just one day after the summit concluded—FBI agents executed an arrest. Court records filed under the slightly misspelled name "Edward Dobrovsky" revealed charges of cyber extortion and conspiracy.

Centralization and Court Actions
Following his apprehension, a 54-year-old Dubrovsky was initially booked into a federal detention facility in Philadelphia, as logged by the U.S. Bureau of Prisons inmate locator. However, the legal proceedings shifted rapidly. On October 9, a formal notice was entered moving the case docket to the U.S. District Court for the Eastern District of Texas.
Legal experts and sources close to the probe note that the Eastern District of Texas has taken absolute command of the broader ShinyHunters investigative portfolio. At the time of reporting, Dubrovsky remained unrepresented by counsel, awaiting an official court-appointed public defender or retained attorney.
The Domino Effect: International Arrests
Dubrovsky’s arrest does not occur in a vacuum; it is the latest in a sweeping series of coordinated international strikes against the ShinyHunters syndicate and its facilitators:
- September 2026: Dutch police apprehended Pepijn van der Stap, a reformed hacker turned cybercriminal, seizing a cache of digital devices that FBI investigators have spent weeks poring over.
- Early October 2026: Reuters reported that a teenager operating under the alias "Rey"—identified as Saif Al-din Khader and believed to have assumed leadership of ShinyHunters following Van der Stap’s arrest—was detained and began cooperating with federal authorities. Khader’s apprehension occurred as the group attempted to extort a navigation and digital aviation unit recently divested by aerospace giant Boeing in late 2025.
- October 8, 2026: Edward Dubrovsky is arrested in Pennsylvania, signaling that federal authorities are increasingly scrutinizing the gray-market ecosystem of ransomware negotiators and corporate intermediaries.
Supporting Context & Metrics: The Anatomy of ShinyHunters
To understand the gravity of Dubrovsky’s arrest, one must examine the operational blueprint of the ShinyHunters group and the sheer financial and operational devastation they have wreaked upon global enterprises and government institutions alike.
Modus Operandi
ShinyHunters has historically relied on sophisticated phishing campaigns, credential-stuffing attacks, and the theft of authentication tokens to breach corporate environments, particularly Software-as-a-Service (SaaS) providers. Once inside, the group exfiltrates vast repositories of proprietary and personal data, establishing heavy leverage before threatening to leak the information publicly on dark web forums or dedicated leak sites unless exorbitant ransom demands are satisfied.
Financial Impact and Metrics
- $70 Million Extorted: According to internal FBI tracking estimates, the ShinyHunters collective has successfully coerced victims into paying more than $70 million in ransoms throughout the year 2026 alone.
- The FBI Breach: In an unprecedented breach of law enforcement infrastructure, ShinyHunters managed to siphon sensitive data from the FBI’s online recruitment portal. The compromised files exposed detailed personnel metrics, including unit assignments, professional specializations, and deeply personal medical and psychiatric documentation of thousands of active agents.
- The Boeing Spin-Off Incident: Just prior to the series of international arrests, the group targeted a newly independent digital aviation unit spun off from Boeing, demonstrating their aggressive appetite for high-value corporate targets.
The Paradox of the Negotiator
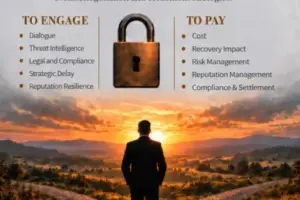
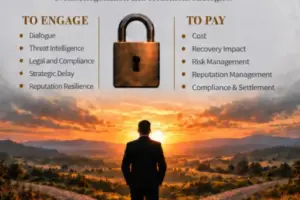
The arrest of a prominent negotiation executive highlights the complex ethical and legal gray zones inherent in modern incident response. Dubrovsky is the author of Cyber Extortion Strategic Response, a 252-page manual designed to guide organizations through the labyrinth of ransomware negotiations.
In promotional materials for his book, Dubrovsky emphasized a critical strategic distinction:

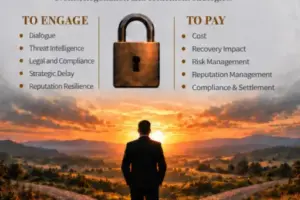
"Communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
While such advisory services are standard practice within the multi-billion-dollar cyber insurance and incident response industry, federal investigators are increasingly examining whether certain intermediaries cross the legal threshold from advisory compliance into illegal facilitation, extortion conspiracy, or money laundering on behalf of criminal enterprises.
Official Statements and Institutional Silence
The response from official channels has been tightly controlled, reflecting the extreme sensitivity of an investigation that directly compromises federal law enforcement personnel files.
- FBI Director Kash Patel: Released a brief statement via Twitter/X confirming the arrest of a Canadian individual in connection with the ShinyHunters probe, though the initial announcement refrained from naming the suspect or disclosing specific corporate affiliations.
- The Federal Bureau of Investigation: Field offices in both Pennsylvania and Texas have officially declined to comment on the ongoing litigation, citing active court seals on core components of the indictment.
- Cypfer and CyberSteward: Cypfer issued a clarifying public statement noting that Dubrovsky was never a founder or co-founder—contrary to claims on his professional networking profiles—and that he had permanently severed ties with the firm upon his resignation in November 2025. CyberSteward has not yet issued a formal public statement regarding the arrest of its affiliated team member, though inquiries remain ongoing.
Future Outlook: What Lies Ahead
As the legal proceedings against Edward Dubrovsky transition to the Eastern District of Texas, the cybersecurity and incident response industries are bracing for profound shockwaves.
- Scrutiny on Ransomware Intermediaries: The arrest signals a potential paradigm shift in how the U.S. Department of Justice views third-party ransomware negotiators. Firms that facilitate communication between corporate victims and threat actors may face heightened regulatory compliance standards and rigorous federal audits to ensure their operations do not inadvertently aid and abet criminal conspiracies.
- Unsealing of Indictments: Legal analysts anticipate that as jurisdictional motions settle in Texas, federal prosecutors will gradually unseal core components of the complaint. This is expected to shed light on the specific evidentiary links connecting Dubrovsky’s professional activities to the digital infrastructure of the ShinyHunters syndicate.
- Wider Industry Fallout: With sources indicating that additional charges against principals at other ransomware advisory firms may be forthcoming, corporate boards and risk management officers are recalibrating their incident response strategies. The fear of criminal liability for engaging with sanctioned threat actors or negotiating extortion demands introduces unprecedented risk into corporate crisis management.
The war against ShinyHunters has evolved from a traditional digital manhunt into a complex geopolitical and legal battleground. As federal investigators continue to mine the digital footprints seized from overseas raids and domestic arrests, the boundaries between legitimate cybersecurity defense and illicit cybercrime facilitation have never been more perilously blurred.