In an extraordinary twist that blurs the lines between cybersecurity defenders and the cybercriminals they track, federal law enforcement has arrested a prominent Canadian cybersecurity executive on charges tied to the notorious ShinyHunters hacking syndicate. The high-stakes arrest comes at a humiliating time for U.S. national security: the very same threat group recently breached the Federal Bureau of Investigation (FBI), making off with sensitive personnel dossiers detailing thousands of agents, their units, specialized assignments, and deeply personal medical and psychiatric records.
Federal court records, combined with intelligence gathered from multiple sources close to the sprawling international investigation, confirm that Edward Dubrovsky—a 54-year-old security professional, author, and prominent figure in ransomware response—was taken into custody by FBI agents in Pennsylvania. Dubrovsky’s arrest was not random. He had traveled to Philadelphia to attend and sponsor the prestigious Cyber Risk Summit, a major cyber-insurance conference held at the Loews Philadelphia Hotel.
While the initial public announcements from federal authorities and The New York Times kept the suspect’s identity under wraps, subsequent court filings and investigative reporting exposed the dramatic descent of an executive who literally wrote the book on navigating digital extortion. Dubrovsky now faces severe federal charges, including conspiracy to commit cyber extortion and interference with commerce by threats.
The case highlights a growing, systemic vulnerability in the modern threat landscape: the murky ecosystem surrounding ransomware negotiation firms. As law enforcement intensifies its dragnet against ShinyHunters—a syndicate that has allegedly hauled in upwards of $70 million in illicit ransoms this year alone—investigators are increasingly scrutinizing whether third-party advisory firms cross the ethical and legal threshold from remediation experts into facilitators of extortion.
Detailed Chronology: From the Philadelphia Summit to Federal Custody
The Trap at the Cyber Risk Summit (October 5–7, 2026)
The sequence of events leading to Dubrovsky’s arrest culminated during the first week of October 2026 in Philadelphia, Pennsylvania. According to event schedules and online disclosures, the Cyber Risk Summit drew elite figures from the cyber insurance, risk mitigation, and incident response sectors.
Dubrovsky, operating under his newly established Canadian security firm CyberSteward—and previously tied as a managing director to another major conference sponsor, Cypfer—was an active participant. Sources close to the investigation indicate that federal agents had been tracking Dubrovsky’s movements closely. They moved in to effect the arrest as he networked with industry peers, dealing a stunning blow to the executive’s professional reputation.
The Charges and Judicial Transfer (October 8–9, 2026)
On October 8, federal prosecutors filed formal charges against the defendant under the slightly misspelled name Edward Dobrovsky. The core complaint, which has largely been sealed to protect ongoing intelligence operations, charges the defendant with:
- Conspiracy to threaten to impair the confidentiality of information with the intent to extort money
- Interference with commerce by threats
Public court docket entries indexed at CourtListener trace the rapid legal maneuvering that followed. Although a 54-year-old Edward Dubrovsky was initially booked and held at a federal detention facility in Philadelphia according to the U.S. Bureau of Prisons inmate locator, a transfer notice was filed on October 9.
The case was swiftly moved to the U.S. District Court for the Eastern District of Texas, a jurisdiction that sources confirm has become the centralized nerve center for the multi-agency prosecution of the ShinyHunters network. As of press time, Dubrovsky remains unrepresented by a permanent attorney, with court-appointed legal counsel yet to be finalized.
Supporting Context & Metrics: Inside the ShinyHunters Syndicate
To understand the gravity of Dubrovsky’s arrest, one must examine the operational blueprint of the ShinyHunters group and the cascading series of international law enforcement actions that cornered them.

Phishing, SaaS Exploitation, and a $70 Million Haul
ShinyHunters has long operated as one of the most destructive and agile cybercriminal cartels in the digital ecosystem. Their methodology typically relies on sophisticated spear-phishing campaigns and stolen enterprise credentials. By infiltrating corporate accounts at major software-as-a-service (SaaS) providers, they harvest proprietary databases, intellectual property, and sensitive customer records, holding them hostage under the threat of public leaks.
According to conservative estimates released by federal investigators, ShinyHunters has successfully extorted more than $70 million from corporate and institutional victims during the 2026 calendar year alone.
The European Connection: Pepijn van der Stap
The current wave of arrests began to build momentum in September 2026, when Dutch law enforcement authorities executed a targeted raid that resulted in the arrest of Pepijn van der Stap, a reformed hacker turned cybercriminal suspected of playing a foundational role in the ShinyHunters apparatus.
Sources indicate that FBI investigators immediately seized and began poring over digital devices recovered during the Dutch operation. The data extracted from Van der Stap’s hardware provided the critical digital breadcrumbs that linked international ransomware facilitators—such as advisory executives—directly to the core operational nodes of the hacking syndicate.
The Rise and Fall of "Rey"
The situation escalated dramatically following Van der Stap’s apprehension. A younger, highly aggressive faction leader operating under the digital moniker "Rey" assumed tactical control of ShinyHunters.
Displaying an unprecedented level of bravado, Rey began actively taunting federal authorities. In a devastating breach that exposed deep vulnerabilities within national security frameworks, ShinyHunters successfully raided an FBI online recruitment portal. The stolen cache included deeply sensitive background information on thousands of active-duty and applicant agents, encompassing unit assignments, operational specialties, and confidential medical and psychiatric histories.
The brazen taunting, however, proved to be Rey’s undoing. Investigative journalism by Reuters and follow-up reporting revealed that "Rey" was actually a teenager named Saif Al-din Khader. Khader was quickly tracked down, detained, and—according to unfolding reports—is currently cooperating with federal investigators. The noose tightened around Khader just as the group attempted a botched extortion campaign against a major navigation and digital aviation unit recently spun off by Boeing in late 2025.
Official Statements and Corporate Fallout
The silence from official federal channels has been deafening, underscoring the extreme sensitivity of an ongoing investigation involving a compromised national security intelligence apparatus.
The FBI Maintains Silence
When contacted for comment regarding Dubrovsky’s arrest and its direct relation to the ShinyHunters data breach, representatives for the FBI declined to provide statements. A brief statement posted to X (formerly Twitter) by FBI Director Kash Patel acknowledged overarching progress in cracking down on international cyber syndicates but omitted specific details regarding the Canadian executive’s capture or the scope of the internal security breach.
Cypfer and CyberSteward Distance Themselves
The arrest sent shockwaves through the niche market of cyber extortion advisory and ransomware negotiation firms. Dubrovsky, who built a substantial personal brand around incident management, is the author of Cyber Extortion Strategic Response, a 252-page textbook published to guide organizations through the complex ethics and legalities of ransom negotiations.

An excerpt from the book’s promotional material highlights the fine line Dubrovsky routinely lectured on:
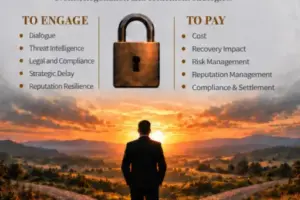
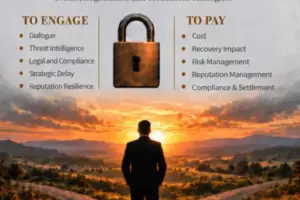
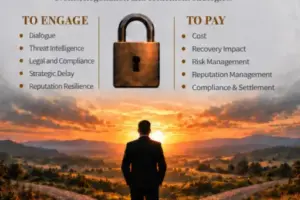
"At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
However, federal prosecutors appear to believe Dubrovsky crossed the boundary from analytical engagement into active criminal conspiracy.
In the wake of his arrest, corporate entities scrambled to manage their public relations. While LinkedIn profiles and historical company data initially linked Dubrovsky as a co-founder of Cypfer, a corporate spokesperson issued a swift clarification to the press: Cypfer asserted that Dubrovsky was never a founder or co-founder, but rather a managing director who resigned from the firm in December 2025. Following his departure, Dubrovsky aligned himself with CyberSteward, another security consultancy that was co-sponsoring the Philadelphia summit.
Future Outlook: A Turning Point in Ransomware Investigations
The arrest of Edward Dubrovsky marks a watershed moment in the global fight against cybercrime, signaling a profound shift in how law enforcement views the gray-market ecosystem of ransomware negotiations.
For years, third-party mediation firms have operated in a regulatory vacuum. Tasked by panicked corporations with lowering ransom demands, verifying proof-of-life for stolen data, and quietly settling extortion claims in cryptocurrency, these firms have sat at the intersection of illegal extortion and legitimate corporate risk management.
Legal experts and cyber intelligence analysts anticipate that Dubrovsky’s trial in the Eastern District of Texas will establish monumental legal precedents regarding the criminal liability of advisory personnel. Furthermore, insiders close to the investigation suggest that Dubrovsky’s case is merely the tip of the iceberg; federal prosecutors are reportedly preparing additional indictments targeting high-ranking principals at competing ransomware negotiation firms who allegedly facilitated extortion payouts for cartel syndicates.
As the FBI works desperately to secure its compromised internal databases and mitigate the fallout from the ShinyHunters leaks, the prosecution of an elite incident response expert serves as a chilling warning to the cybersecurity industry: the legal shield protecting ransomware negotiators is fracturing, and the DOJ is no longer drawing a distinction between the hackers holding the keys and the advisors paying the toll.